Tag Archives: Nessus

New vulnersBot for Telegram with advanced searches and subscriptions

New vulnersBot for Telegram with advanced searches and subscriptions. Vulners.com team have recently presented a new version of vulnerability intelligence bot for Telegram messenger. Now you can search for vulnerabilities and other security content by talking with bot.

Searches

For example, I’ve heard about new critical vulnerability in Samba called SambaCry by analogy with famous WannaCry. Let’s see what Vulners knows about it.
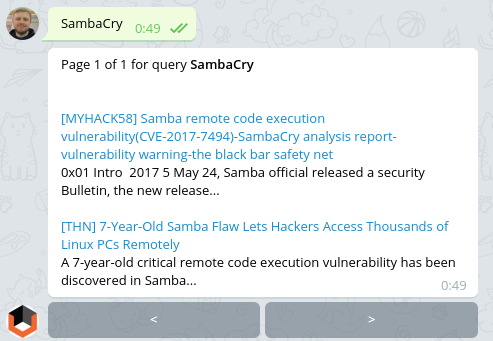
SambaCry Vulners Bot Search

Ok, I see it has id CVE-2017-7494. Do we have exploits related to this vulnerability?
cvelist:CVE-2017-7494 AND bulletinFamily:”exploit”
Continue reading →

WannaCry about Vulnerability Management

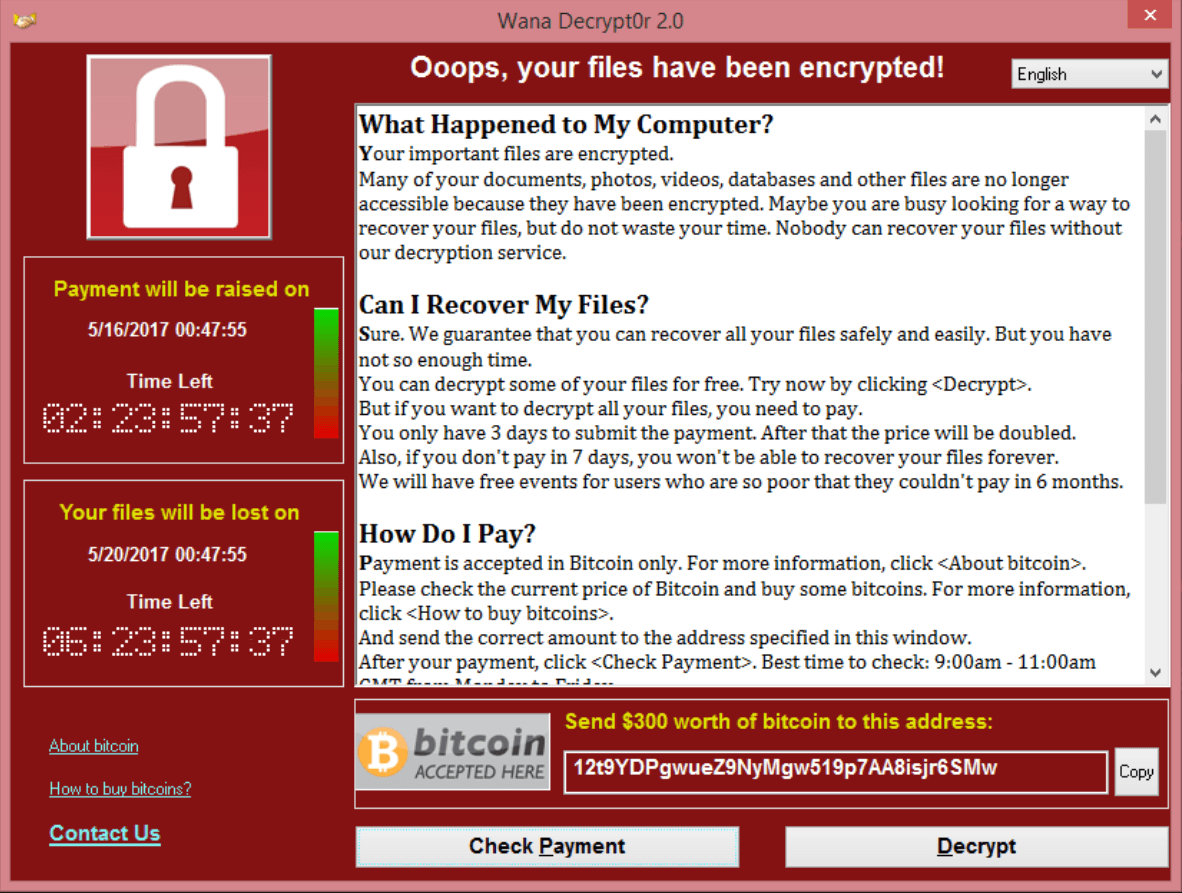
WannaCry about Vulnerability Management. Nearly all mainstream media wrote today about massive ransomware attacks around the world: 16 medical institutions in UK, strong rumours that huge companies in Russia, and even Russian Ministry of Internal Affairs suffered a damage.

At this moment Kaspersky recorded more than 45,000 attacks in 74 countries around the world, but mostly in Russia. During the attack WannaCry malware encrypts data with the extension “.WCRY” added to the filename – that’s why it is called this way.

WannaCry CryptoLocker

What I like in this WannaCry story, that it’s actually all about Vulnerability Management.

Continue reading →

Rapid7 Nexpose in 2017

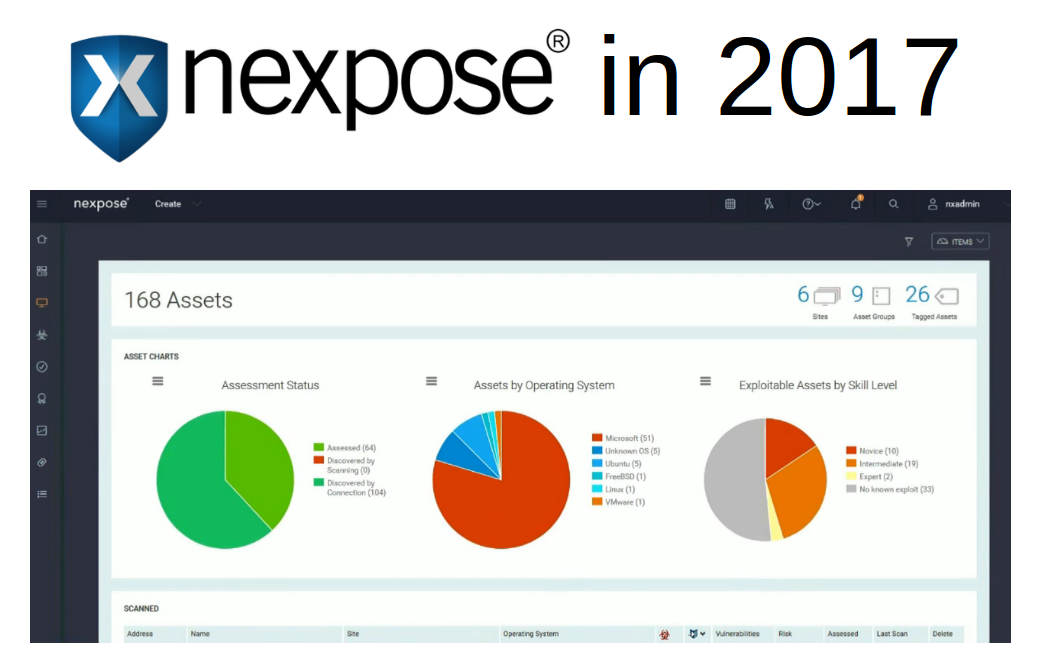
Rapid7 Nexpose in 2017. Last year I tested Rapid7 Nexpose and wrote two posts about installation and use of Nexpose Community Edition and Nexpose API. I didn’t follow news of this vendor for a about year. Today I watched live demo of Nexpose latest version. It has some new interesting features, improvements and ideas, that I would like to mention.

Rapid7 Nexpose in 2017

And of course, things that sales people say to you should be always taken with some skepticism. Only concrete implementation tested in your environment matters. But they usually mention some useful ideas that can be perceived independently from the products they promote.
Continue reading →

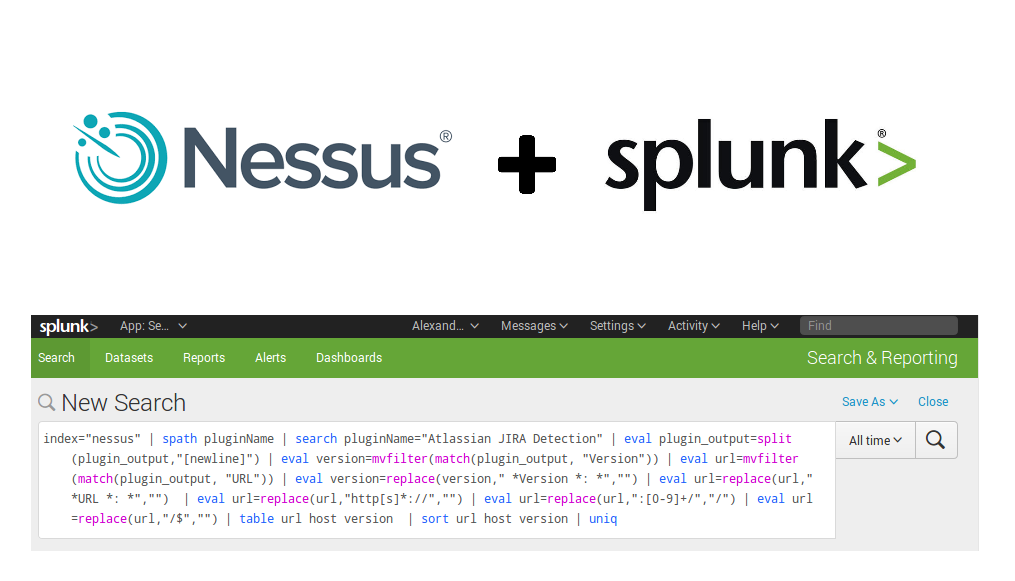
Tracking software versions using Nessus and Splunk

Tracking software versions using Nessus and Splunk. Let’s say you have already exported scan results from Nessus or Tenable SecurityCenter to Splunk using HTTP event connector, or in some other way. And you see that some critical software vulnerability was published. For example, this month Jira critical vulnerability. How to find out, do we have vulnerable servers in our infrastructure or not?

Nessus plus Splunk

Of course we can start a new Nessus scan to detect vulnerable hosts. However, Nessus plugin for this particular vulnerability may be released with a big latency and you will not find this vulnerability in your scans. So, it’s may be faster just to search for detected Jira servers in available scan results using Splunk searching mechanism.

Continue reading →

Vulners Subsriptions and Apache Struts RCE

Vulners Subsriptions and Apache Struts RCE. If you work in IT Security Department of any large software developing company, you were probably searching for Apache Struts in your environment on this week.

And it’s all because of CVE-2017-5638:

Apache Struts is a free, open-source, Model-View-Controller (MVC) framework for creating elegant, modern Java web applications, which supports REST, AJAX, and JSON.
In a blog post published Monday, Cisco’s Threat intelligence firm Talos announced the team observed a number of active attacks against the zero-day vulnerability (CVE-2017-5638) in Apache Struts

This is a good example, that shows the usefulness of the Vulners.com service.

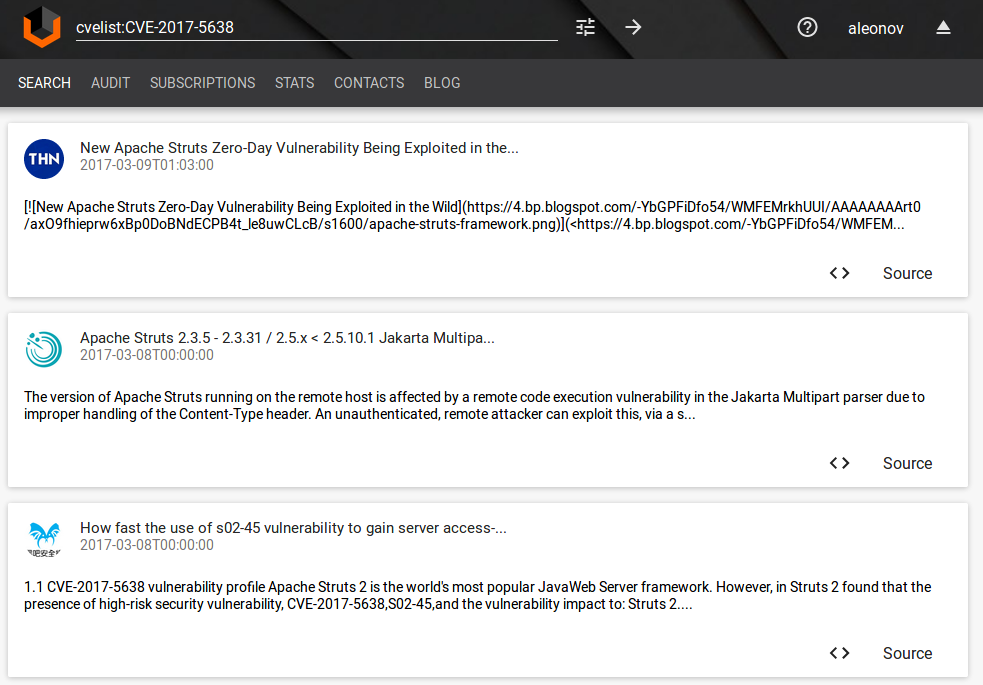
Just open cvelist:CVE-2017-5638 query and you will see all the objects related to this issue. This request works even before this CVE number appear on NVD and Mitre databases!

Vulners Apache Struts2 RCE

Here are: description of the vulnerability from The Hacker News, manual on how to use this vulnerability to gain server access from myhack58, Nessus local windows and remote cgi detection plugins.

Continue reading →

What's actually new in Tenable.io VM application

What’s actually new in Tenable.io VM application. My last post was about the structure of a new Tenable.io cloud platform. Now, let’s see what is actually new in Tenable.io Vulnerability Management application.

Tenable.io VM is obviously based on Nessus Cloud, which in its turn had features similar to Nessus Manager briefly reviewed earlier. So, today I want to concentrate only on new features.

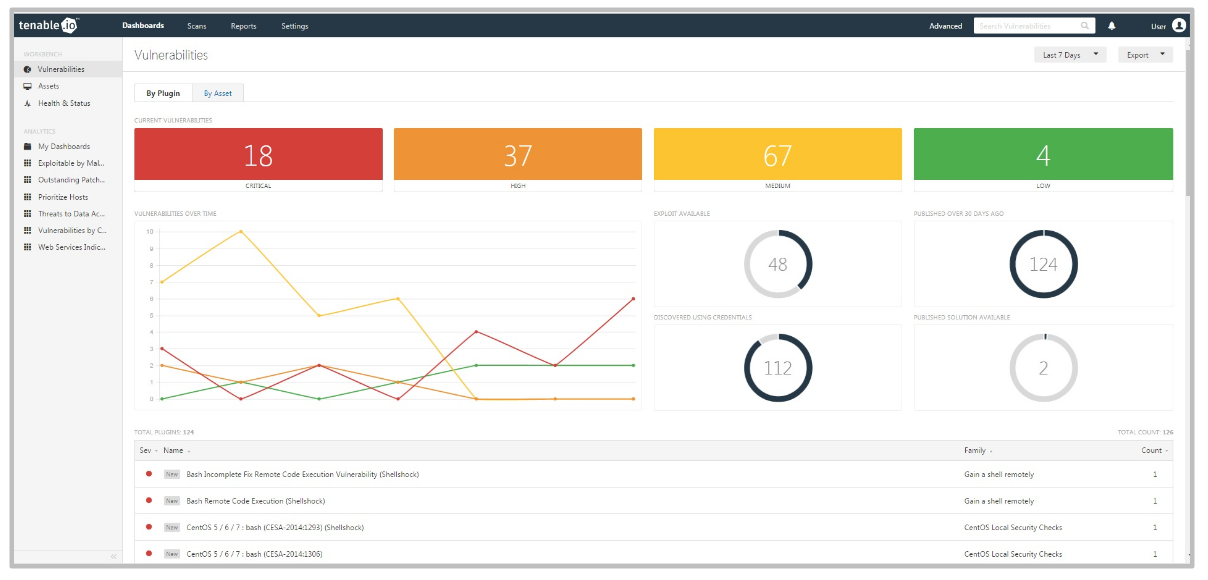
Tenable.io VM

According to the public interface screenshots and Tenable.io datasheets, it will have some new dashboards and reports, free integration with PVS and Nessus deployed on-premise, and something very new in asset management.

Continue reading →