Tag Archives: OOM

About Remote Code Execution - PHP "PHP2Shell" (CVE-2026-109618, CVE-2026-109619) vulnerabilities

About Remote Code Execution - PHP PHP2Shell (CVE-2026-109618, CVE-2026-109619) vulnerabilities

About Remote Code Execution - PHP "PHP2Shell" (CVE-2026-109618, CVE-2026-109619) vulnerabilities. PHP is a popular server-side programming language. The vulnerabilities, covered in the October Linux Patch Wednesday, allow unauthenticated remote code execution through specially crafted requests. CVE-2026-109618 is caused by improper OOM error handling, while CVE-2026-109619 is caused by a use-after-free vulnerability in PHP's global data structures. Exploitation can lead to system compromise, data theft, malware installation, and access to internal networks.

⚙️ The PHP Foundation had known about the root cause since 2024 but prioritized a fix only on August 11, 2026. Updates planned for October 22 were released a day early due to an embargo breach. Users should upgrade to PHP 8.5.12, 8.4.27, 8.3.36, or 8.2.35, or install patched Linux distribution packages. For unsupported branches, migration to a supported version is recommended. Meanwhile, restrict Internet access and apply configuration-based workarounds. For network devices, install vendor fixes or apply recommended mitigations.

Positive Technologies implemented protections using PT AF, PT NAD, and PT NGFW, and released detection rules for MaxPatrol VM.

🛠 GitHub hosts over 1,000 public PHP2Shell exploit repositories, but achieving RCE against a specific target remains difficult. Exploitation requires a tailored exploit compatible with the target's PHP build, SAPI, extensions, and runtime configuration.

👾 Both vulnerabilities were added to CISA KEV on October 26. Confirmed exploitation remains limited, mostly involving network devices.

On October 26, Dream Group reported attacks on Palo Alto Networks devices in the US, Japan, Taiwan, and South Korea. Attackers identified 240 targets among 19,000 devices and compromised 24 firewalls and one management server. Three reportedly belonged to US government infrastructure. The attacks exploited PHP2Shell and the Linux kernel LPE vulnerability Fragnesia (CVE-2026-46300). Attackers stole service account credentials, user and group lists, network configurations, and private keys.

On November 12, Check Point experts reported attacks against Security Gateway devices that had started on October 30. By exploiting PHP2Shell and the DynamicCLI LPE vulnerability (CVE-2026-123039), attackers gained initial access, escalated their privileges, and installed the TSGA backdoor along with its network component, TSProxy. During the destructive phase of the attacks, they also gained SSH access to a VMware ESXi host and executed the destroy_v6 wiper.

🌐 According to Censys data, 27 million PHP services exposed to the Internet remain unpatched. In addition, the vulnerabilities affect products from numerous vendors, including Palo Alto Networks, Check Point, Netgate, Coolify, and Cisco.
October Linux Patch Wednesday

October Linux Patch Wednesday

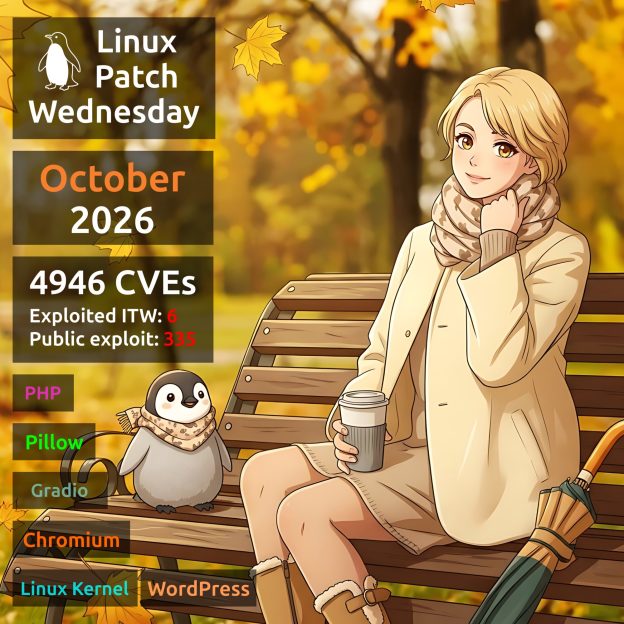
October Linux Patch Wednesday. There are 4,946 vulnerabilities in total. By comparison, there were 2,653 in September. That's an 86% increase! This time, there are 1,954 vulnerabilities in the Linux Kernel and 814 in Chromium. Together, they make up 56% of all vulnerabilities.

Six vulnerabilities show signs of being exploited in the wild:

🔻 RCE - PHP "PHP2Shell" (CVE-2026-109618, CVE-2026-109619). PHP is a popular programming language widely used for web application development. CVE-2026-109618 is an out-of-memory (OOM) handling vulnerability that allows remote code execution when an application receives a specially crafted request. CVE-2026-109619 is a use-after-free vulnerability that allows PHP to access stale references to freed memory, potentially leading to remote code execution. Linux distributions began releasing patches on the day the vulnerabilities were disclosed, October 21. More than 470 links to public exploits are available on GitHub. Both vulnerabilities were added to the CISA KEV on October 26.

🔻 SFB - Linux Kernel "PwnEscape" (CVE-2026-99999). The vulnerability affects the Linux kernel's networking stack and allows an attacker inside a KVM guest virtual machine to corrupt the host kernel's memory. This could expose sensitive host memory contents or cause the host system to crash. Researchers demonstrated a complete escape from a guest VM to the host. Linux distributions began releasing patched packages on October 16, and public exploits appeared on GitHub the same day. The vulnerability was added to the VulnCheck KEV on October 19.

🔻 RCE - WordPress (CVE-2026-87902). WordPress is a popular content management system (CMS) for building websites and blogs. Under certain conditions, this vulnerability allows an unauthenticated attacker to execute arbitrary code remotely on the server. Public exploits have been available on GitHub since September 22. The vulnerability was added to the CISA KEV on September 25. Debian released patched packages on September 28.

🔻 XSS - WordPress "Comment2Shell" (CVE-2026-93485). The vulnerability allows an unauthenticated attacker to inject JavaScript code through a specially crafted comment. The code is executed in the browser when an administrator views the comment, allowing the attacker to hijack his session and potentially execute arbitrary code on the server. The vulnerability was added to the VulnCheck KEV on September 18. Public exploits have been available on GitHub since September 22. Patched packages have been available in Debian since September 28.

🔻 AFR - Gradio (CVE-2026-28414). Gradio is a Python library for quickly building machine learning interfaces. The vulnerability allows unauthenticated attackers to read arbitrary files from a Windows server running Python 3.13 or later, even when Gradio authentication is enabled. A public exploit appeared on February 27. The vulnerability was added to the VulnCheck KEV on May 31. ALT Linux has been providing patched packages since October 1.

Another 335 vulnerabilities have no known signs of exploitation in the wild, but public exploits are available for them. Notable examples include:

🔸 EoP - Linux Kernel (CVE-2026-98260). This use-after-free vulnerability in the POSIX CPU timers mechanism allows a local unprivileged user to escalate privileges to root. Researcher v4bel demonstrated a root shell on Ubuntu 26.04 running kernel 7.0.0-30-generic as part of the Infinity Core project. The exploit is also reported to enable container escapes and privilege escalation on Android. Patched packages have been available since October 15. A public exploit was published on GitHub on October 17.

🔸 RCE - Pillow (CVE-2026-112900). Pillow is a Python library for image processing. An attacker can upload an EPS file to execute arbitrary code on the server. Patched packages have been available in Debian since October 21. Public exploits have been available on GitHub since October 23.

🗒 Full Vulristics report (ZIP; 1.7 MB)