Tag Archives: RCE

Vulristics Microsoft Patch Tuesday July 2021: Zero-days EoP in Kernel and RCE in Scripting Engine, RCEs in Kernel, DNS Server, Exchange and Hyper-V

Vulristics Microsoft Patch Tuesday July 2021: Zero-days EoP in Kernel and RCE in Scripting Engine, RCEs in Kernel, DNS Server, Exchange and Hyper-V. Hello everyone! For the past 9 months, I’ve been doing Microsoft Patch Tuesday reviews quarterly. Now I think it would be better to review the July Patch Tuesday while the topic is still fresh. And that will save us some time in the next Last Week’s Security news episode. So, July Patch Tuesday, 116 vulnerabilities.

The 2 most critical are the Windows Kernel Elevation of Privilege Vulnerabilities (CVE-2021-31979, CVE-2021-33771). These vulnerabilities are critical because they are used in real attacks according to Microsoft’s Threat Intelligence Center and Security Response Center. Tenable: “A local, authenticated attacker could exploit these vulnerabilities to run processes with elevated permissions. Similar zero-day vulnerabilities were patched in April 2020, which were observed under active exploitation by Google Project Zero.”
Continue reading →

Vulristics: Microsoft Patch Tuesdays Q2 2021

Vulristics: Microsoft Patch Tuesdays Q2 2021. Hello everyone! Let’s now talk about Microsoft Patch Tuesday vulnerabilities for the second quarter of 2021. April, May and June. Not the most exciting topic, I agree. I am surprised that someone is reading or watching this. For me personally, this is a kind of tradition. Plus this is an opportunity to try Vulristics in action and find possible problems. It is also interesting to see what VM vendors considered critical back then and what actually became critical. I will try to keep this video short.

First of all, let’s take a look at the vulnerabilities from the April Patch Tuesday. 108 vulnerabilities, 55 of them are RCEs. Half of these RCEs (27) are weird RPC vulnerabilities. “Researcher who reported these bugs certainly found quite the attack surface”. The most critical vulnerability is RCE in Exchange (CVE-2021-28480). This is not ProxyLogon, this is another vulnerability. ProxyLogon was in March. And this vulnerability is simply related to ProxyLogon, so it is believed that it is exploited in the wild as well. In the second place this Win32k Elevation of Privilege (CVE-2021-28310). It is clearly mentioned in several sources as being used in real attacks. “Bugs of this nature are typically combined with other bugs, such as a browser bug or PDF exploit, to take over a system”. And the only vulnerability with a public exploit is the Azure DevOps Server Spoofing (CVE-2021-28459). Previously known as Team Foundation Server (​TFS), Azure DevOps Server is a set of collaborative software development tools. It is hosted on-premises. Therefore, this vulnerability can be useful for attackers.

Continue reading →

Vulristics: Microsoft Patch Tuesdays Q1 2021

Vulristics: Microsoft Patch Tuesdays Q1 2021. Hello everyone! It has been 3 months since my last review of Microsoft vulnerabilities for Q4 2020. In this episode I want to review the Microsoft vulnerabilities for the first quarter of 2021. There will be 4 parts: January, February, March and the vulnerabilities that were released between the Patch Tuesdays.

I will be using the reports that I created with my Vulristics tool. This time I’ll try to make the episodes shorter. I will describe only the most critical vulnerabilities. Links to the full reports are at the bottom of the blog post.

Continue reading →

Vulristics Vulnerability Score, Automated Data Collection and Microsoft Patch Tuesdays Q4 2020

Vulristics Vulnerability Score, Automated Data Collection and Microsoft Patch Tuesdays Q4 2020. In this episode I would like to make a status update of my Vulristics project. For those who don’t know, in this project I retrieve publicly available vulnerability data and analyze it to better understand the severity of these vulnerabilities and better prioritize them. Currently, it is mainly about Microsoft Patch Tuesday vulnerabilities, but I have plans to go further. Also in this episode I want to demonstrate the new Vulristics features on Microsoft Patch Tuesday reports for October, November and December 2020.

Vulristics Vulnerability Scores, automated data collection and Microsoft Patch Tuesday Q4 2020

Patch Tuesdays Automated Data Collection

First of all, I dealt with the annoying collecting of the data for Microsoft Patch Tuesdays reports. Previously it took pretty long time. I had to go to Microsoft website and search for CVE IDs. After that, I had to get the comments from various Vulnerability Management vendors and researchers blogs (Tenable, Qualys, Rapid7, ZDI). I wanted this to be as much automated as possible. I have added some code to make CVE search requests on the Microsoft website for a date range (including the second Tuesday of the month). I also figured out how to make searches on the Vulnerability Management vendors blogs. So, now to get a Microsoft Patch Tuesday report it’s only necessary to set the year and month.

Continue reading →

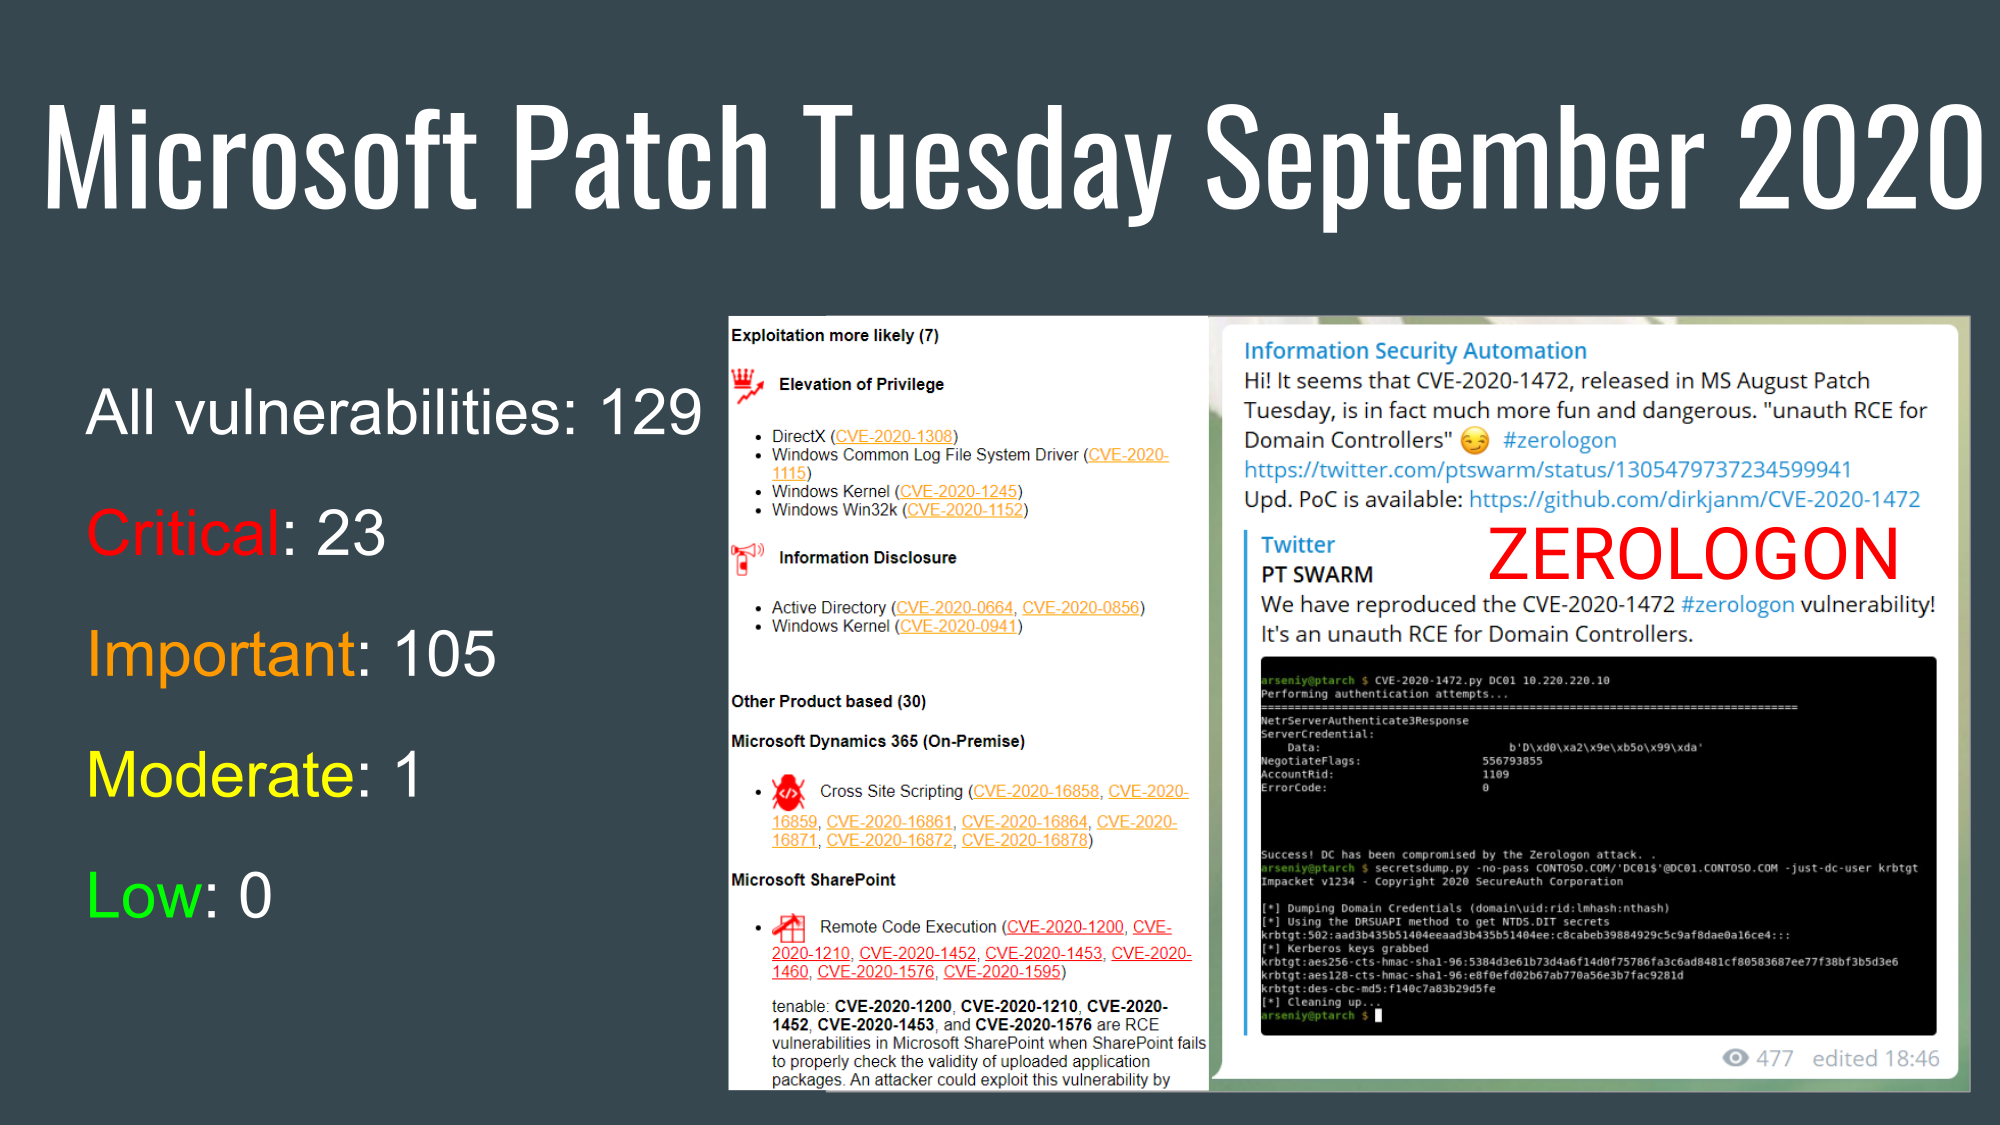
Microsoft Patch Tuesday September 2020: Zerologon and other exploits, RCEs in SharePoint and Exchange

Microsoft Patch Tuesday September 2020: Zerologon and other exploits, RCEs in SharePoint and Exchange. I would like to start this post by talking about Microsoft vulnerabilities, which recently turned out to be much more serious than it seemed at first glance.

Older Vulnerabilities with exploits

“Zerologon” Netlogon RCE (CVE-2020-1472)

One of them is, of course, the Netlogon vulnerability from the August 2020 Patch Tuesday. It’s called “Zerologon”. I would not say that Vulnerability Management vendors completely ignored it. But none of them (well, maybe only ZDI) emphasized in their reports that this vulnerability would be a real disaster.

Continue reading →

Microsoft Patch Tuesday August 2020: vulnerabilities with Detected Exploitation, useful for phishing and others

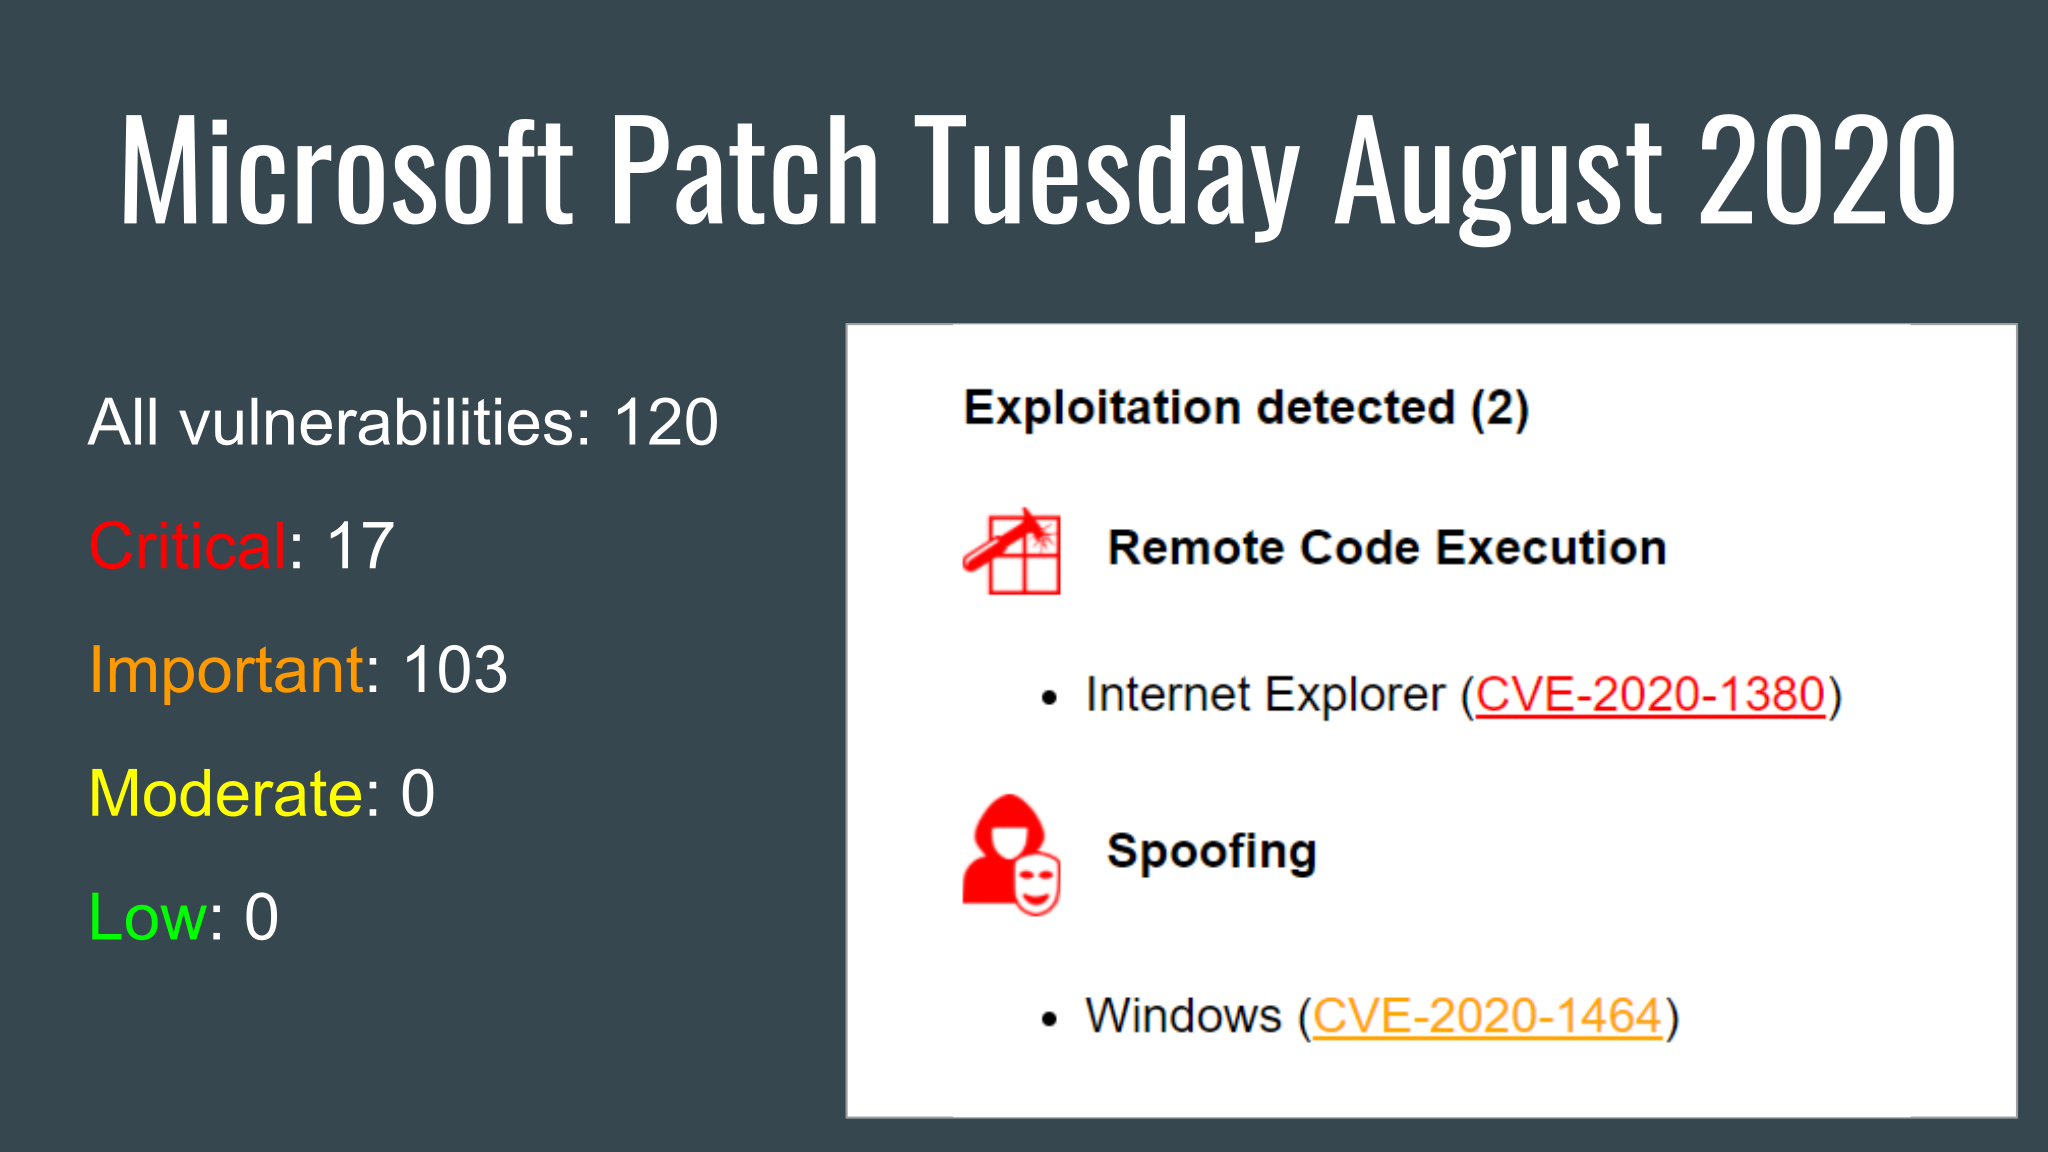
Microsoft Patch Tuesday August 2020: vulnerabilities with Detected Exploitation, useful for phishing and others. This time I would like to review not only the vulnerabilities that were published in the last August Microsoft Patch Tuesday, but also the CVEs that were published on other, not Patch Tuesday, days. Of course, if there are any.

But let’s start with the vulnerabilities that were presented on MS Patch Tuesday on August 11th. There were 120 vulnerabilities: 17 of them are Critical and 103 Important. My vulristics script could not find public exploits for these vulnerabilities on Vulners.com.

Continue reading →

Microsoft Patch Tuesday May 2020: comments from VM vendors, promising stuff for phishing, troubles with SharePoint and lulz with Visual Studio

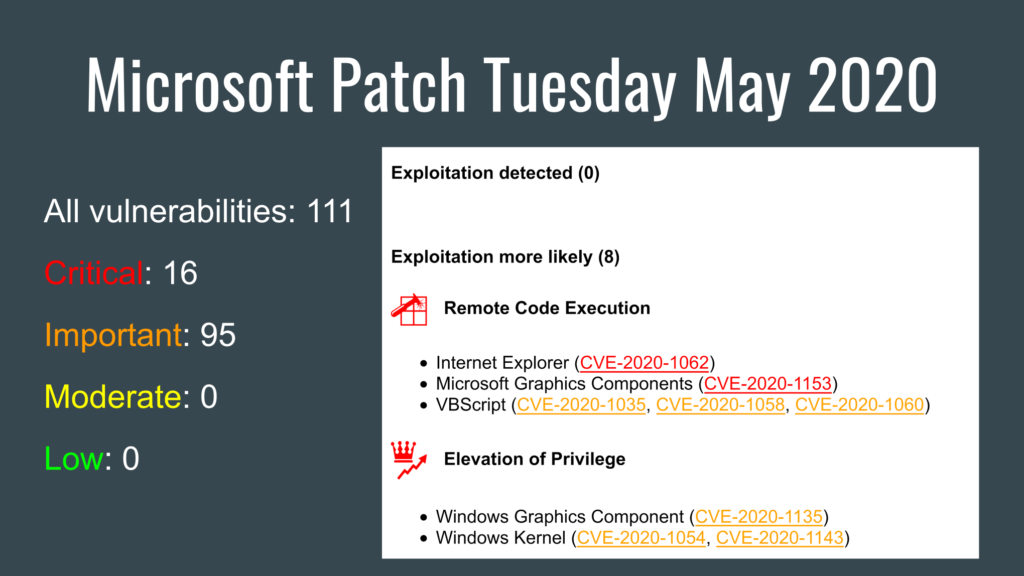
Microsoft Patch Tuesday May 2020: comments from VM vendors, promising stuff for phishing, troubles with SharePoint and lulz with Visual Studio. This will be my third Microsoft Patch Tuesday report in video and audio format. And for the third time in a row, Microsoft has addressed over a hundred vulnerabilities. With my Microsoft Patch Tuesday parser, it was possible to generate a report almost on the same day. But, of course, it takes much more time to describe the vulnerabilities manually.

Microsoft Patch Tuesday May 2020
  • All vulnerabilities: 111
  • Critical: 16
  • Important: 95
  • Moderate: 0
  • Low: 0

Last time I complained that different VM vendors release completely different reports for Microsoft Patch Tuesday. This time I decided that it’s not a bug, but a feature. I upgraded my script to not only show vulnerabilities, but also show how these vulnerabilities were mentioned in the reports of various VM vendors (Tenable, Qualys, Rapid7 and ZDI). In my opinion, it seems pretty useful.

Continue reading →