Tag Archives: SharePoint

April "In the Trend of VM" (#26): one Microsoft SharePoint vulnerability

April In the Trend of VM (#26): one Microsoft SharePoint vulnerability

April "In the Trend of VM" (#26): one Microsoft SharePoint vulnerability. Presenting the traditional monthly roundup of trending vulnerabilities according to Positive Technologies. Once again, it is single-vendor, Microsoft-related, and this time it could not be more compact. While the previous March edition had four trending vulnerabilities, this April edition has only one. In the upcoming May edition, we expect at least three trending vulnerabilities. 😉

🗞 Post on Habr (rus)
🗒 Digest on the PT website (rus)

This vulnerability is from the January Microsoft Patch Tuesday:

🔻 RCE - Microsoft SharePoint (CVE-2026-20963). The vulnerability was initially considered less critical due to an authentication requirement PR:L, but after Microsoft’s reassessment it turned out that authentication is not required for exploitation PR:N. The vulnerability has been added to the CISA KEV, meaning attackers are already exploiting it in the wild. There are no public exploits yet.

🟥 The full list of trending vulnerabilities is available on the portal

April Microsoft Patch Tuesday

April Microsoft Patch Tuesday

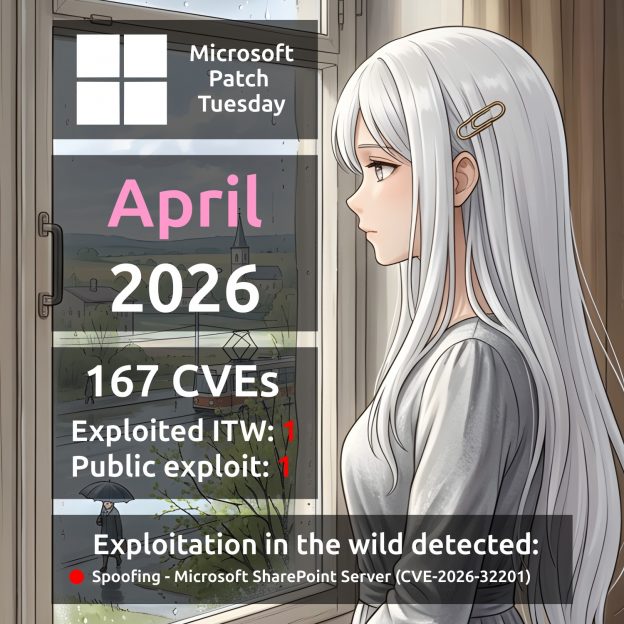
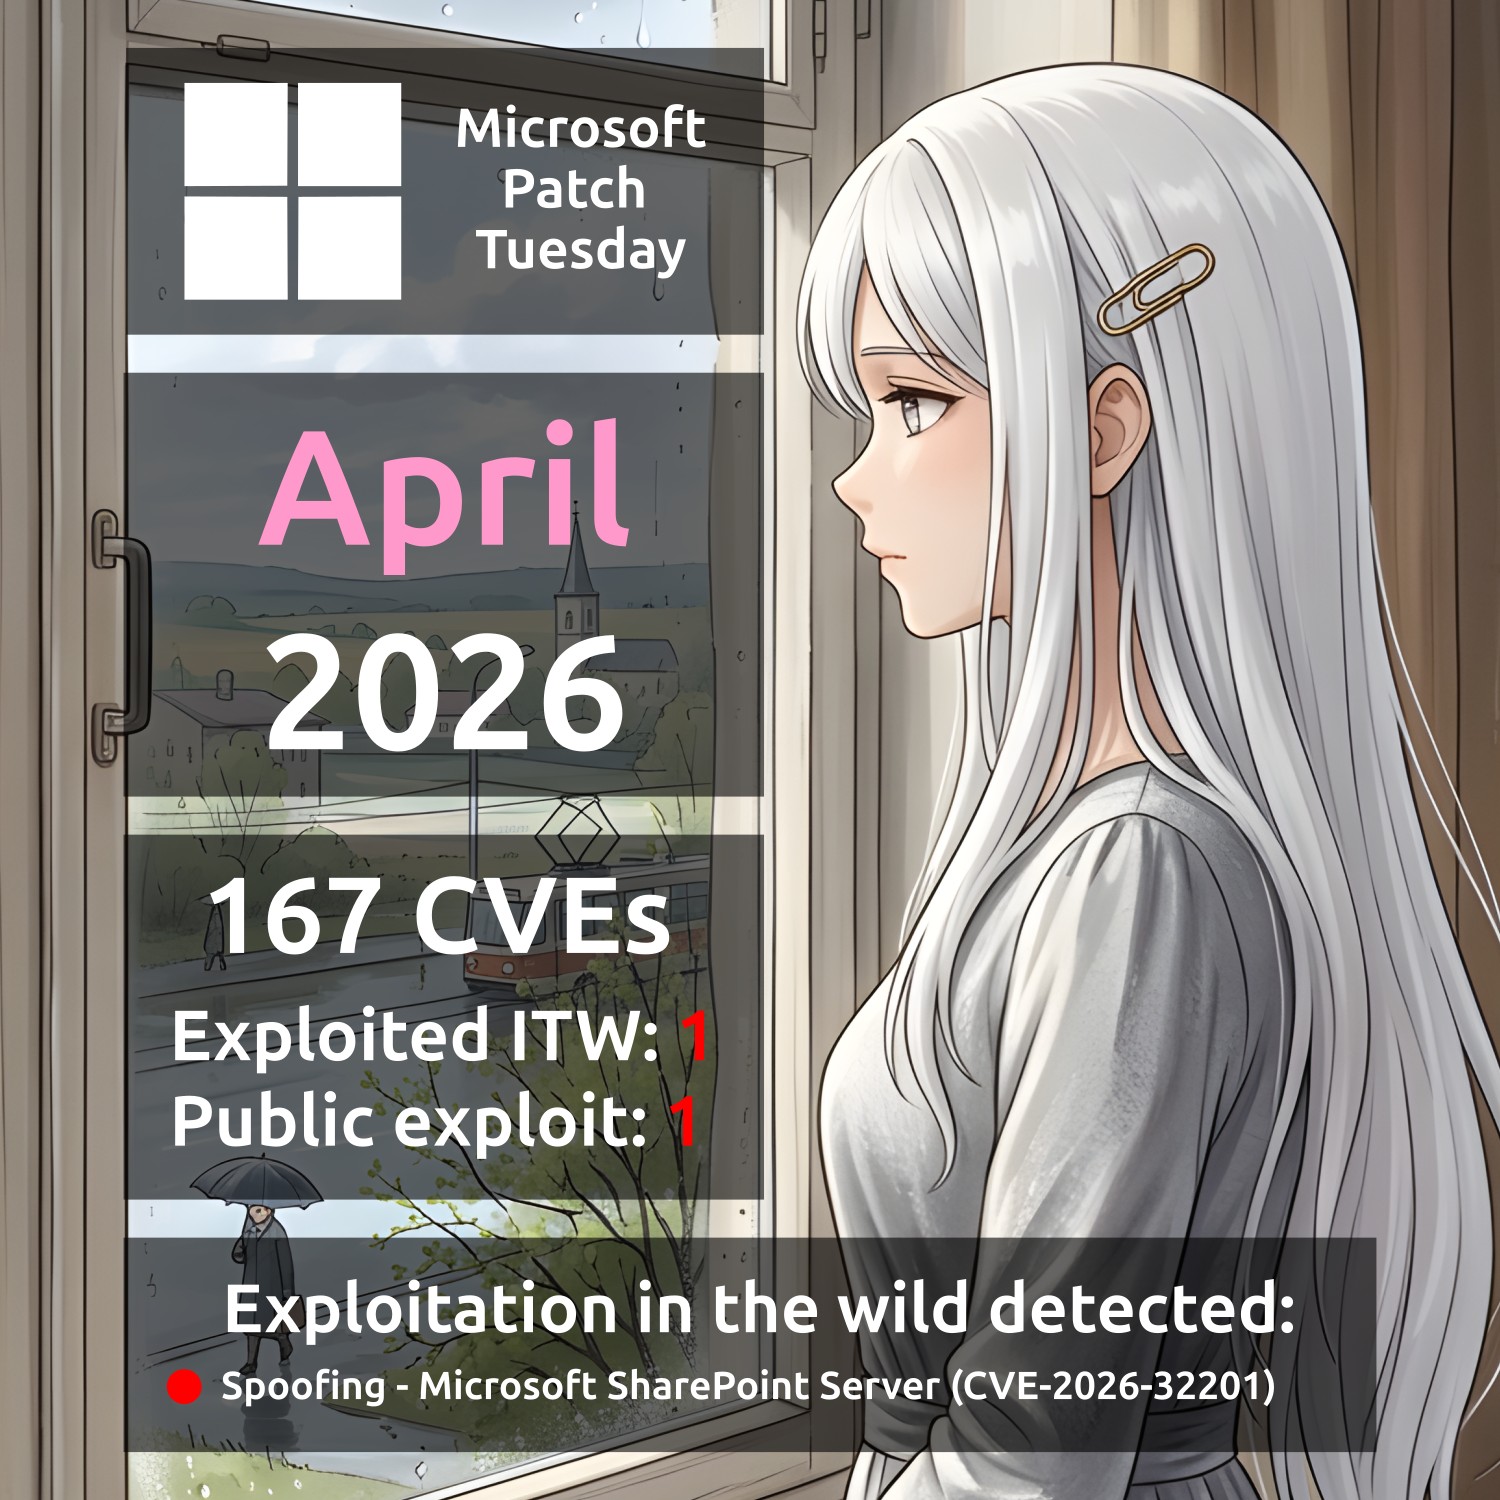
April Microsoft Patch Tuesday. A total of 167 vulnerabilities, about twice as many as in March. There is one vulnerability already being exploited in the wild:

🔻 Spoofing - Microsoft SharePoint Server (CVE-2026-32201). ZDI experts say "Spoofing bugs in SharePoint often manifest as cross-site scripting (XSS) bugs". "An attacker who successfully exploited the vulnerability could view some sensitive information (Confidentiality), make changes to disclosed information (Integrity), but cannot limit access to the resource (Availability)". There is no info yet about how widely it is being used in attacks, but you should not delay patching, especially if SharePoint is exposed to the Internet.

Formally, there are no public exploits yet. However, there are strong indications that a public exploit may already exist for one vulnerability.

🔸 EoP - Microsoft Defender (CVE-2026-33825). "Insufficient granularity of access control" in Microsoft Defender allows a logged-in attacker to gain higher privileges on a local system. Tenable and ZDI say the bug looks similar to the BlueHammer zero-day, for which a public exploit was released on GitHub on April 3. The researcher who published it, Chaotic Eclipse, criticized Microsoft’s disclosure process. ZDI says the exploit is real, but exploitation is unstable and not always reliable.

Other important issues:

🔹 RCE - Windows Active Directory (CVE-2026-33826). To exploit this, the attacker must have an account. The attacker sends a specially crafted RPC request to a vulnerable server, which can lead to code execution. Microsoft says the attacker must be in the same restricted Active Directory domain as the target system.

🔹 RCE - Windows Internet Key Exchange (IKE) Service Extensions (CVE-2026-33824). ZDI says this vulnerability is wormable, meaning it could allow malware to spread automatically between systems. It affects systems with IKE enabled, which creates a large attack surface. Microsoft recommends blocking UDP ports 500 and 4500 at the network edge. However, attackers inside the network can still use it for lateral movement. Patch quickly if you use IKE.

🔹 RCE - Windows TCP/IP (CVE-2026-33827). ZDI also says this may be wormable, especially on systems using IPv6 and IPSec. A race condition makes it harder to exploit, but similar bugs are often exploited at Pwn2Own, so you should not rely on that difficulty. If you use IPv6, test and deploy the patch quickly before exploits appear.

🔹 EoP - Windows Push Notifications (CVE-2026-26167). This Patch Tuesday includes several sandbox escape vulnerabilities, including in Push Notifications, AFD for Winsock, Windows Management Services, and User Interface Core. CVE-2026-26167 (Push Notifications) is the most important because it is the only one with low attack complexity. The others require winning a race condition (AC:H).

🔹 Spoofing - Remote Desktop (CVE-2026-26151). Weak warnings in the Remote Desktop interface allow a network attacker to trick a user into opening a specially crafted file, leading to spoofing. The issue was found by the UK National Cyber Security Centre (NCSC).

🗒 Full Vulristics report

About Remote Code Execution - Microsoft SharePoint (CVE-2026-20963) vulnerability

About Remote Code Execution - Microsoft SharePoint (CVE-2026-20963) vulnerability

About Remote Code Execution - Microsoft SharePoint (CVE-2026-20963) vulnerability. This vulnerability was fixed in the January MSPT. At the time of the MSPT release on January 13, VM vendors did not highlight this vulnerability in their reviews, and Microsoft reported no evidence of exploitation in the wild. The CVSS vector was initially rated as CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:H/I:H/A:H (8.8). The "PR:L" indicates that authentication was required to exploit the vulnerability. However, on March 17, Microsoft updated both the vulnerability description and its CVSS vector. The updated CVSS vector is CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H (9.8). The "PR:N" indicates that authentication is not required for exploitation.

Current vulnerability description:

"Deserialization of untrusted data (CWE-502) in Microsoft Office SharePoint allows an unauthorized attacker to execute code over a network. In a network-based attack, an unauthenticated attacker could write arbitrary code to inject and execute code remotely on the SharePoint Server."

👾 On March 18, the vulnerability was added to the CISA KEV catalog. No detailed information about exploitation is available yet, and there are currently no public exploits. However, in terms of potential impact, this vulnerability may be comparable to last year's RCE "ToolShell" (CVE-2025-49704).

The situation surrounding this vulnerability demonstrates that the criticality of any vulnerability cannot be determined once and for all. Indicators of exploitation in the wild or public exploits may emerge at any time, and the vendor may also revise the vulnerability description and CVSS metrics for various reasons. Therefore, all vulnerabilities detected within an infrastructure must be continuously monitored (either internally or via a VM vendor), with their criticality regularly reassessed and remediation deadlines adjusted accordingly.

Given that the status of any specific vulnerability may change at any time, it is not advisable to dismiss vulnerabilities as definitively non-critical or non-exploitable. A responsible approach assumes that all detected vulnerabilities require remediation, prioritized according to their continuously updated risk levels.

March Microsoft Patch Tuesday

March Microsoft Patch Tuesday

March Microsoft Patch Tuesday. A total of 79 vulnerabilities, about one and a half times more than in February. What's truly unusual is that this time there were no vulnerabilities with signs of exploitation in the wild or a public exploit! 🤔 At least not yet. 😏

The following vulnerabilities can be highlighted:

🔹 RCE - Print Spooler (CVE-2026-23669), Office (CVE-2026-26110, CVE-2026-26113), Excel (CVE-2026-26107, CVE-2026-26108, CVE-2026-26109, CVE-2026-26112), SharePoint Server (CVE-2026-26106, CVE-2026-26114)
🔹 EoP - SQL Server (CVE-2026-21262, CVE-2026-26115, CVE-2026-26116), Windows Kernel (CVE-2026-24287, CVE-2026-24289, CVE-2026-26132), Windows Win32k (CVE-2026-24285), SMB Server (CVE-2026-24294, CVE-2026-26128), Windows Graphics Component (CVE-2026-23668), .NET (CVE-2026-26131)
🔹 DoS - .NET (CVE-2026-26127)

🗒 Full Vulristics report

На русском

November "In the Trend of VM" (#21): vulnerabilities in Windows, SharePoint, Redis, XWiki, Zimbra Collaboration, and Linux

November In the Trend of VM (#21): vulnerabilities in Windows, SharePoint, Redis, XWiki, Zimbra Collaboration, and Linux

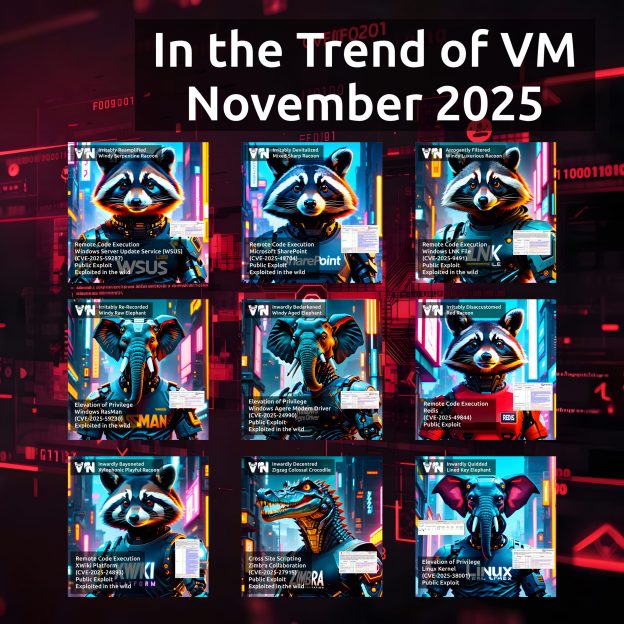
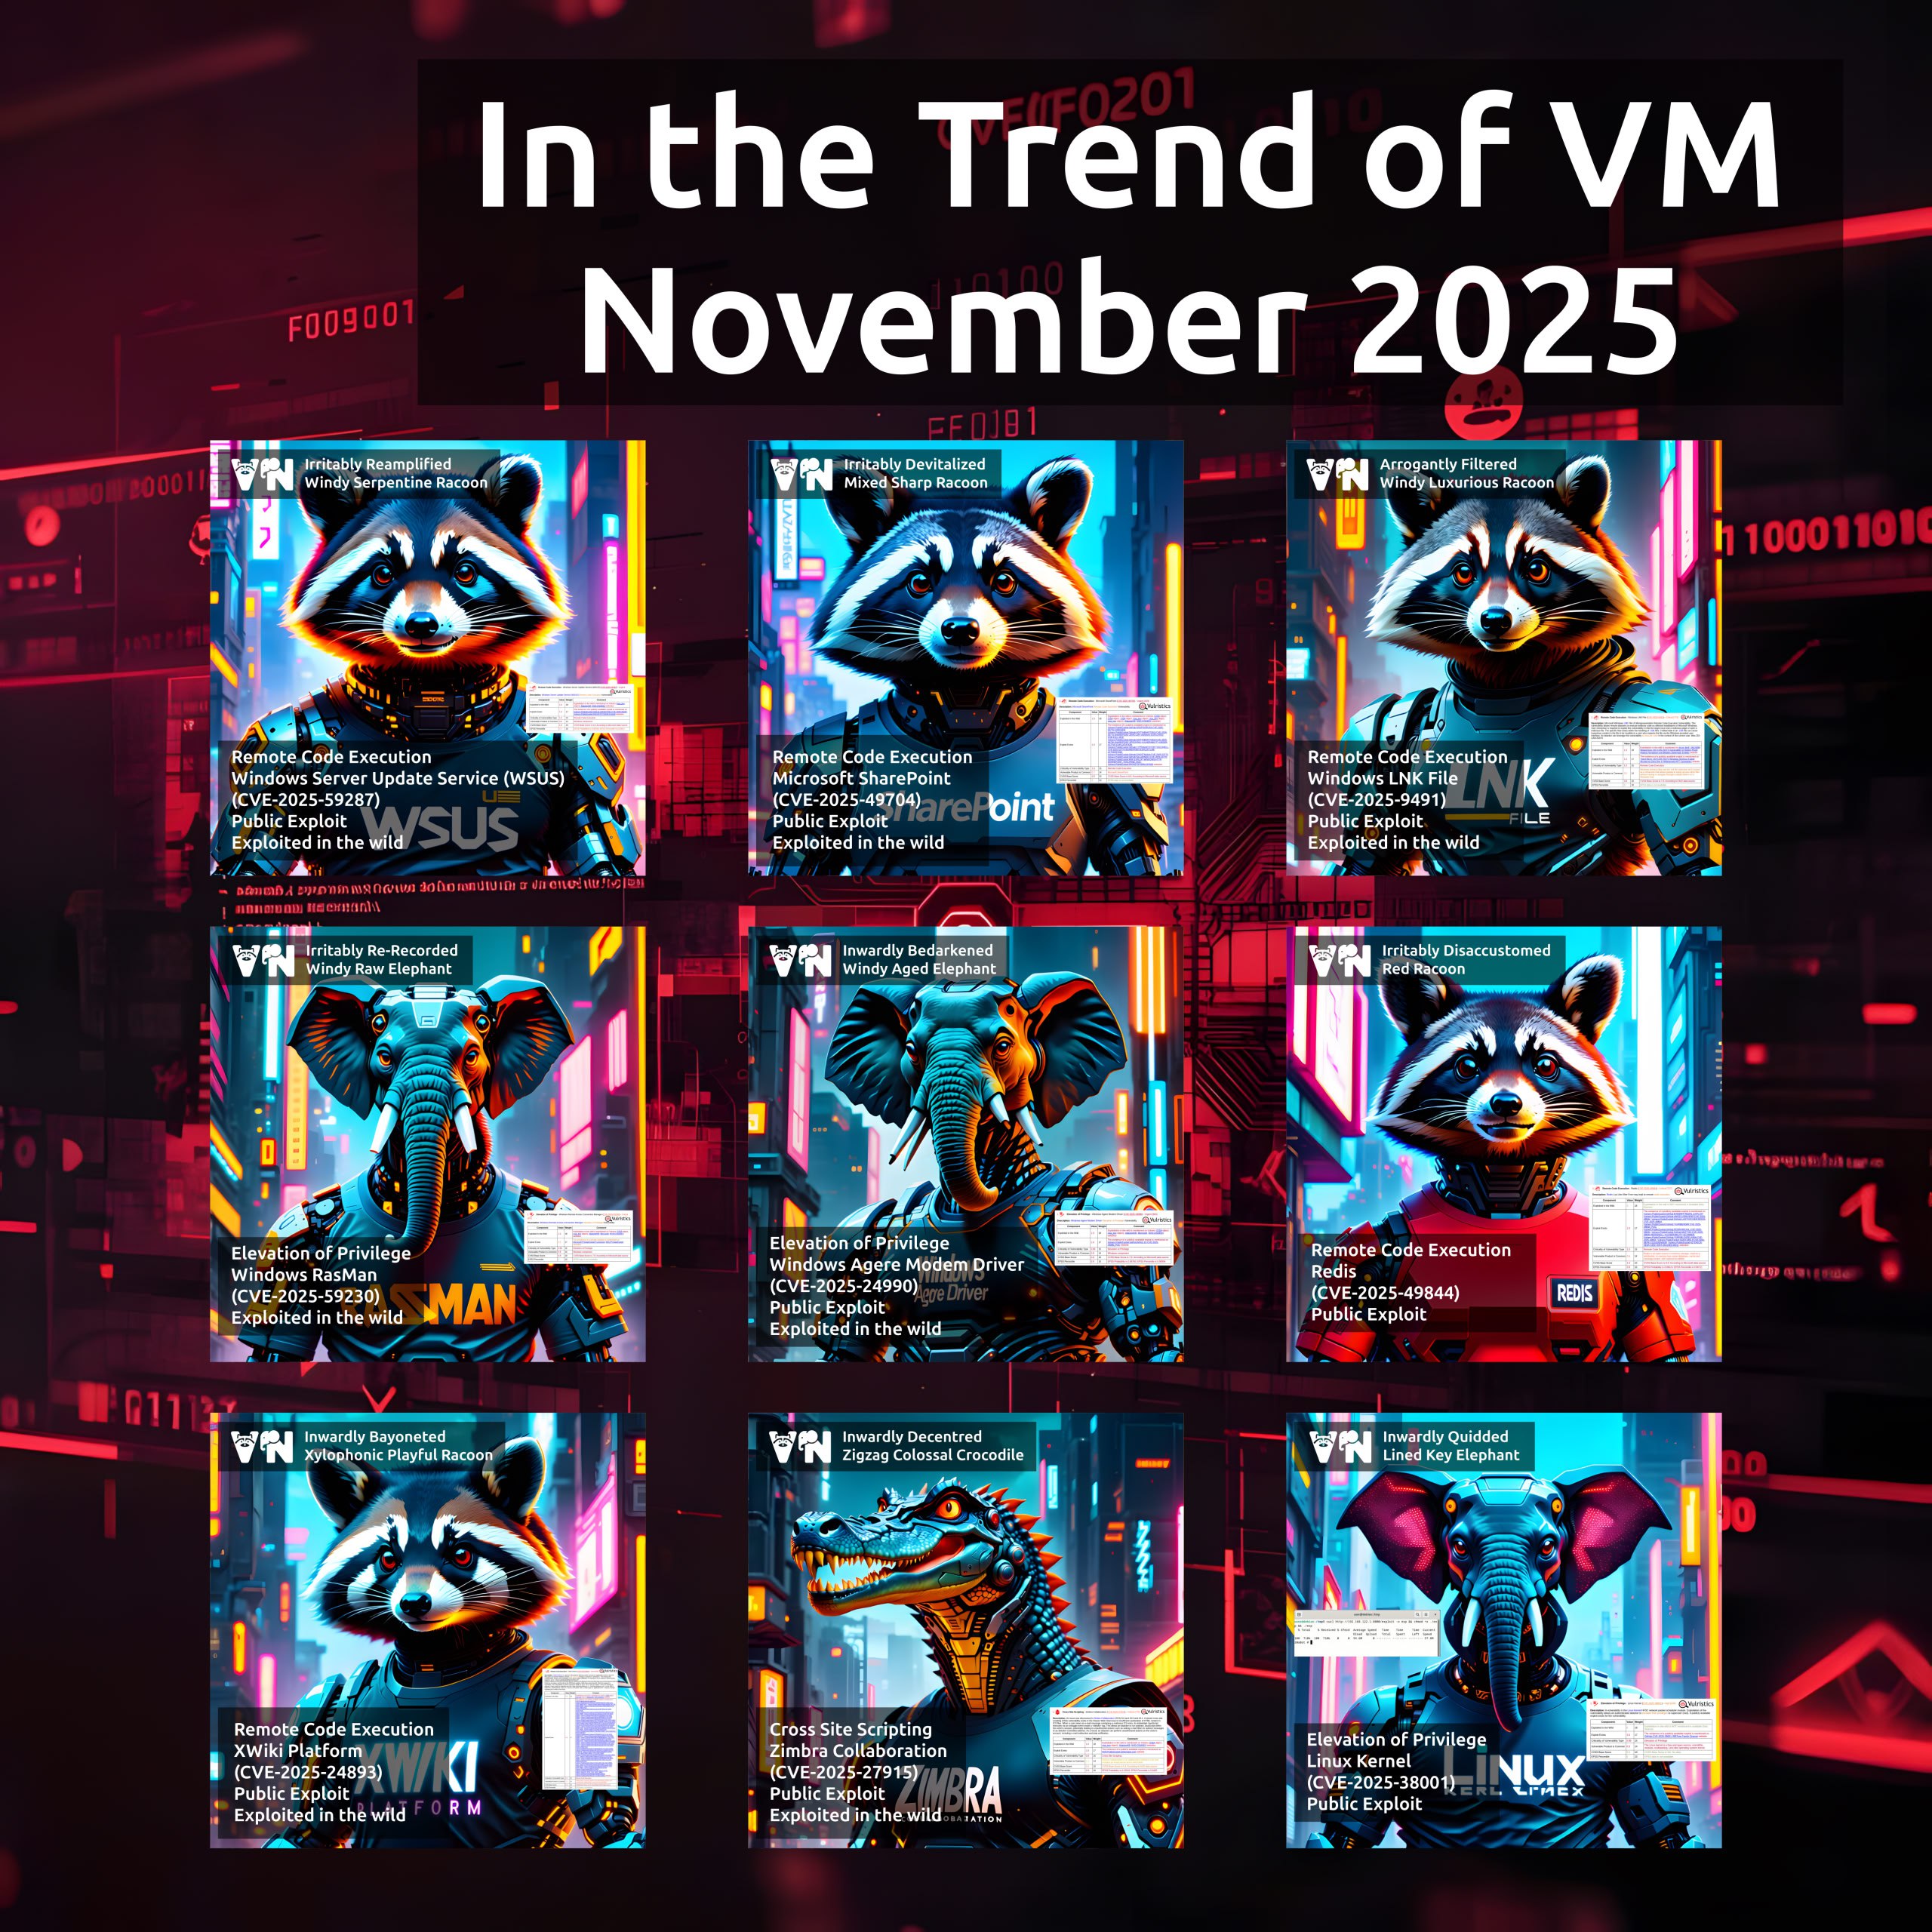
November "In the Trend of VM" (#21): vulnerabilities in Windows, SharePoint, Redis, XWiki, Zimbra Collaboration, and Linux. The usual monthly roundup. After several months, here's a big one. 🔥

🗞 Post on Habr (rus)
🗞 Post on SecurityLab (rus)
🗒 Digest on the PT website (rus)

A total of nine vulnerabilities:

🔻 RCE - Windows Server Update Services (WSUS) (CVE-2025-59287)
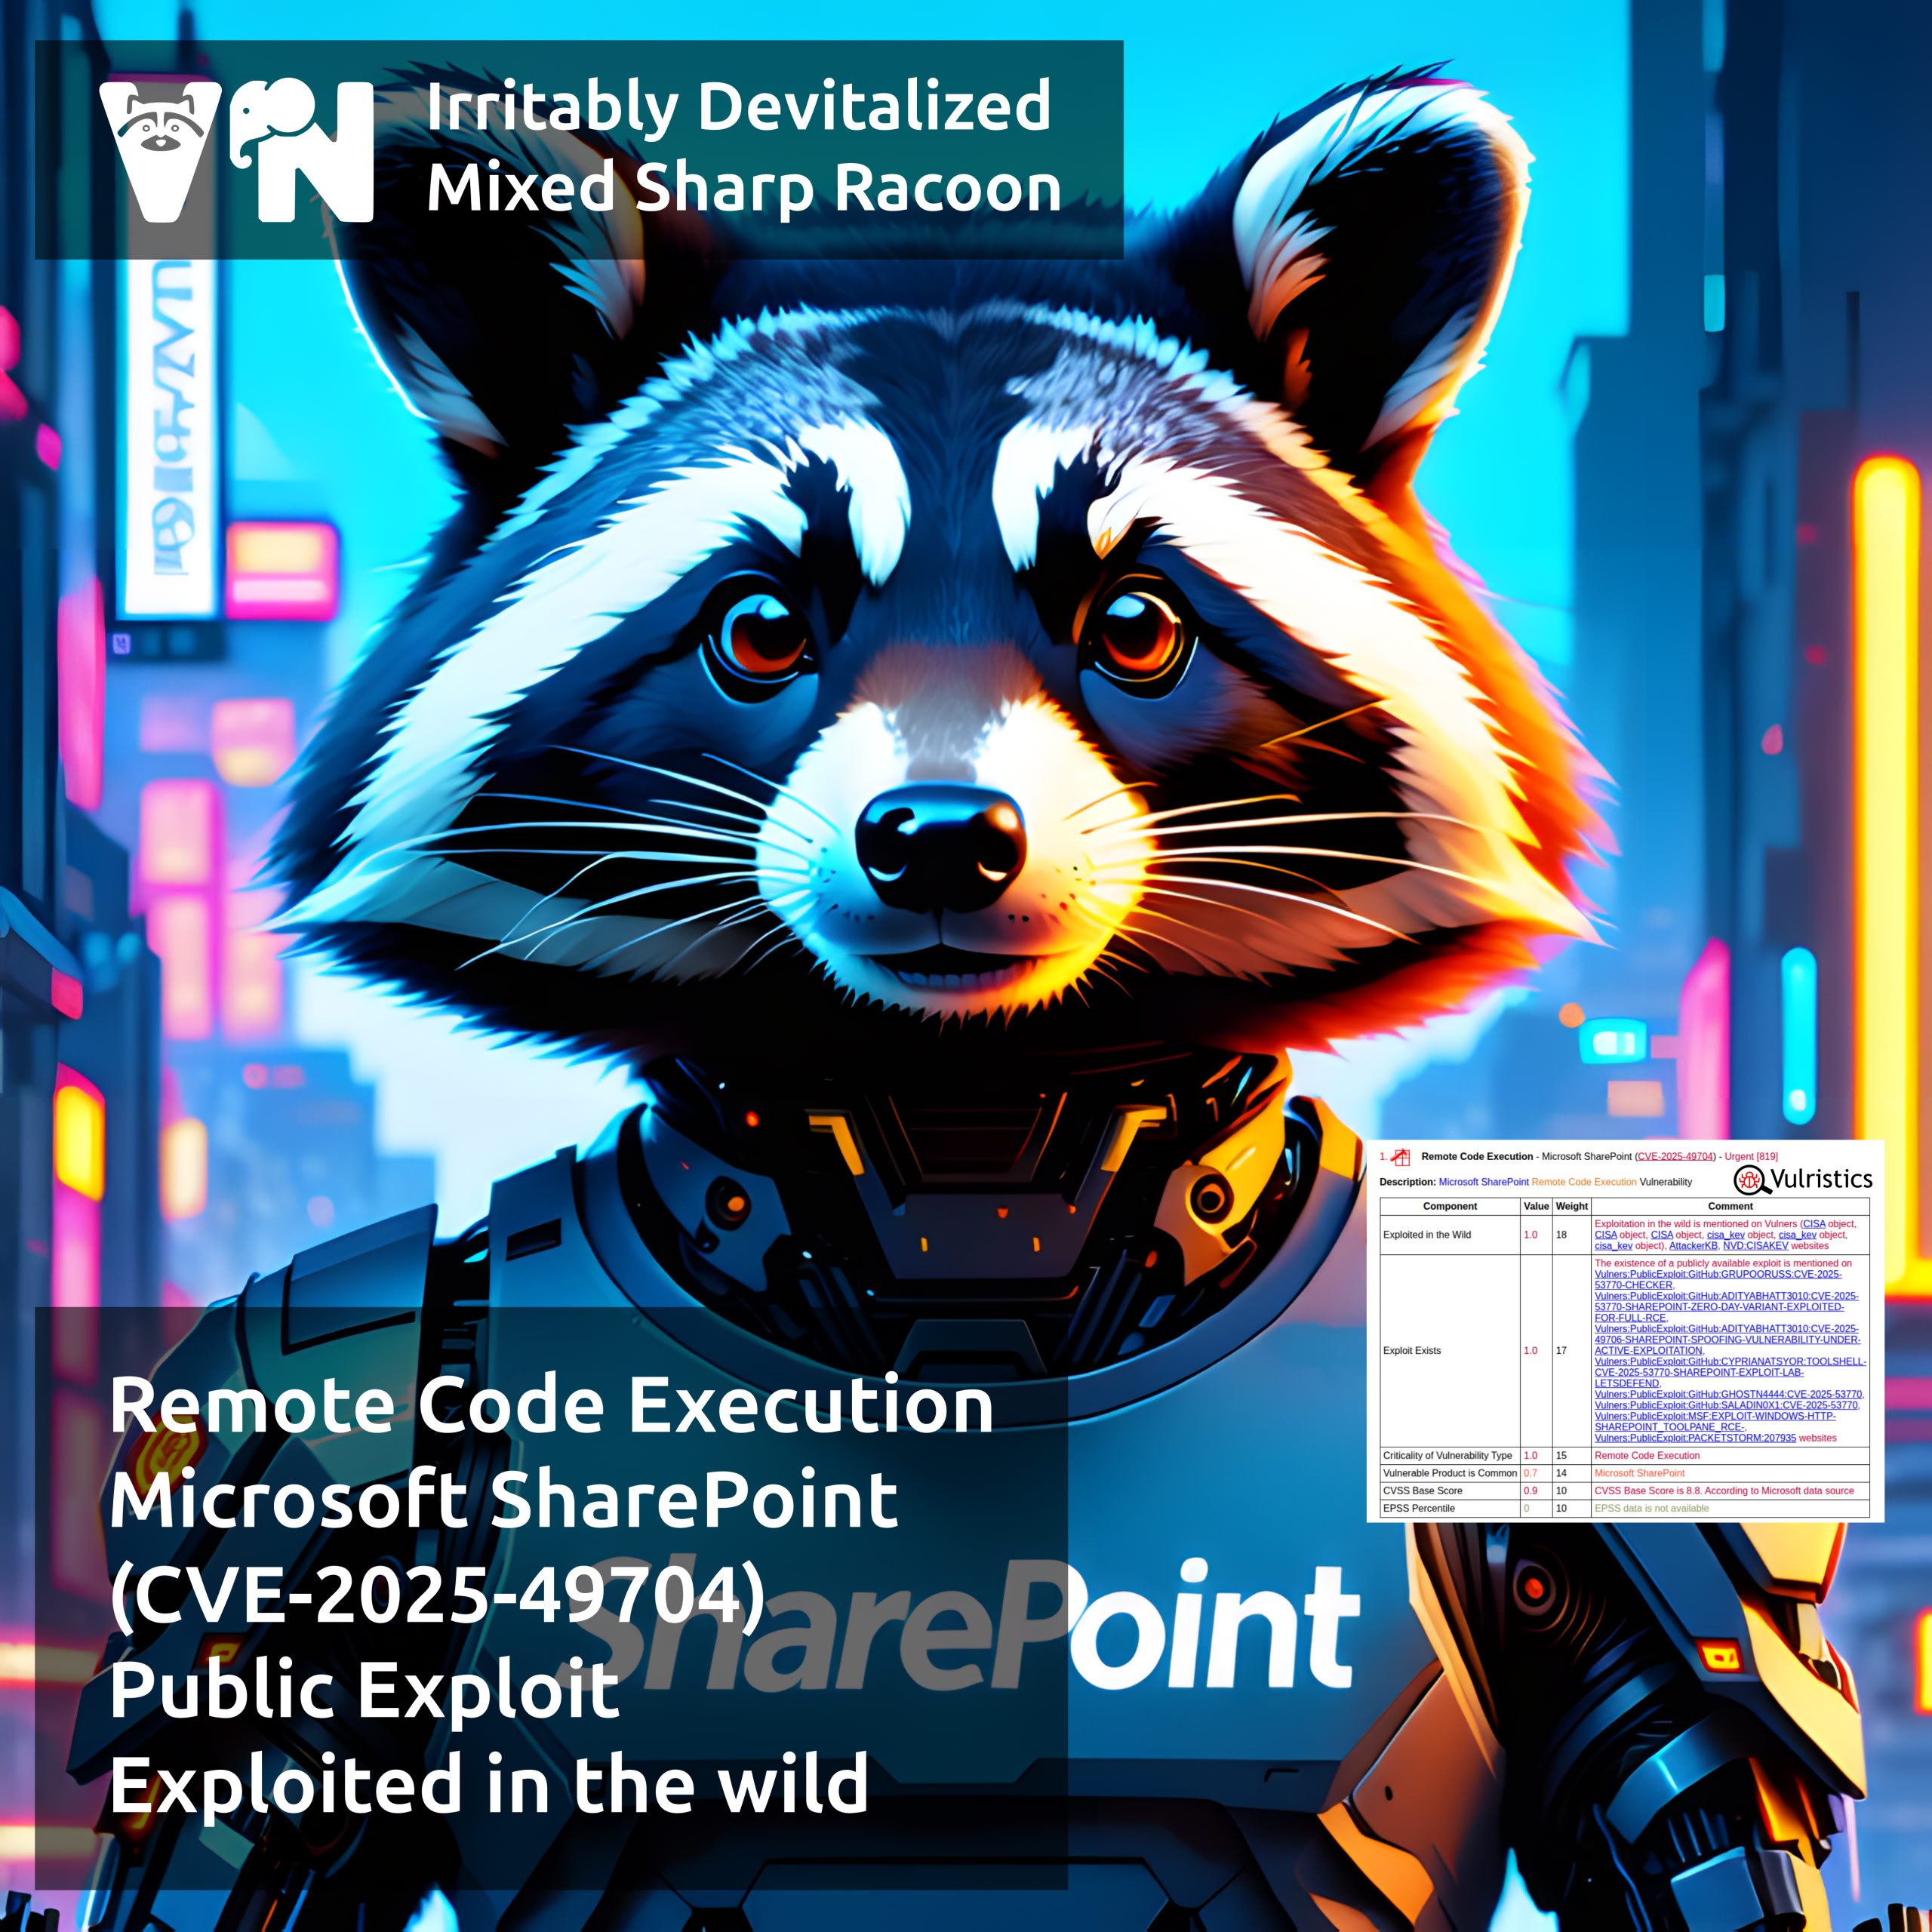
🔻 RCE - Microsoft SharePoint "ToolShell" (CVE-2025-49704)
🔻 RCE - Windows LNK File (CVE-2025-9491)
🔻 EoP - Windows Remote Access Connection Manager (CVE-2025-59230)
🔻 EoP - Windows Agere Modem Driver (CVE-2025-24990)
🔻 RCE - Redis "RediShell" (CVE-2025-49844)
🔻 RCE - XWiki Platform (CVE-2025-24893)
🔻 XSS - Zimbra Collaboration (CVE-2025-27915)
🔻 EoP - Linux Kernel (CVE-2025-38001)

🟥 Trending Vulnerabilities Portal

На русском

About Remote Code Execution - Microsoft SharePoint "ToolShell" (CVE-2025-49704) vulnerability

About Remote Code Execution - Microsoft SharePoint ToolShell (CVE-2025-49704) vulnerability

About Remote Code Execution - Microsoft SharePoint "ToolShell" (CVE-2025-49704) vulnerability. This vulnerability is from the Microsoft's July Patch Tuesday. SharePoint is a web application developed by Microsoft for corporate intranet portals, document management, and collaborative work. Deserialization of untrusted data in the DataSetSurrogateSelector class leads to remote code execution in the context of the SharePoint web server process. Exploitation requires authentication, obtainable for example via CVE-2025-49706 ("ToolShell" chain).

🔬 The "ToolShell" chain was demonstrated by the Viettel Cyber Security team at Pwn2Own Berlin, May 15–17, 2025 (prize $100,000).

👾 Signs of exploitation in the wild have been observed since July 7. The vulnerability was added to CISA KEV on July 22.

🛠 Public exploits available on GitHub since July 21.

➡️ Later "ToolShell" vulnerabilities: CVE-2025-53770 and CVE-2025-53771.

На русском

August Microsoft Patch Tuesday

August Microsoft Patch Tuesday

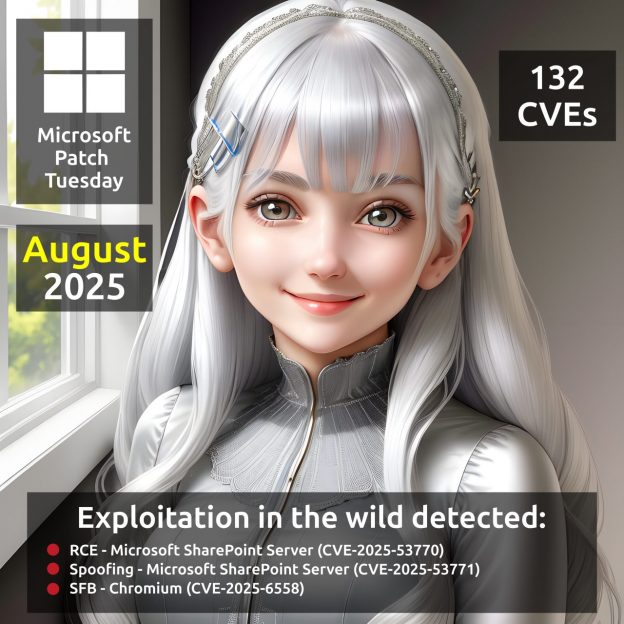
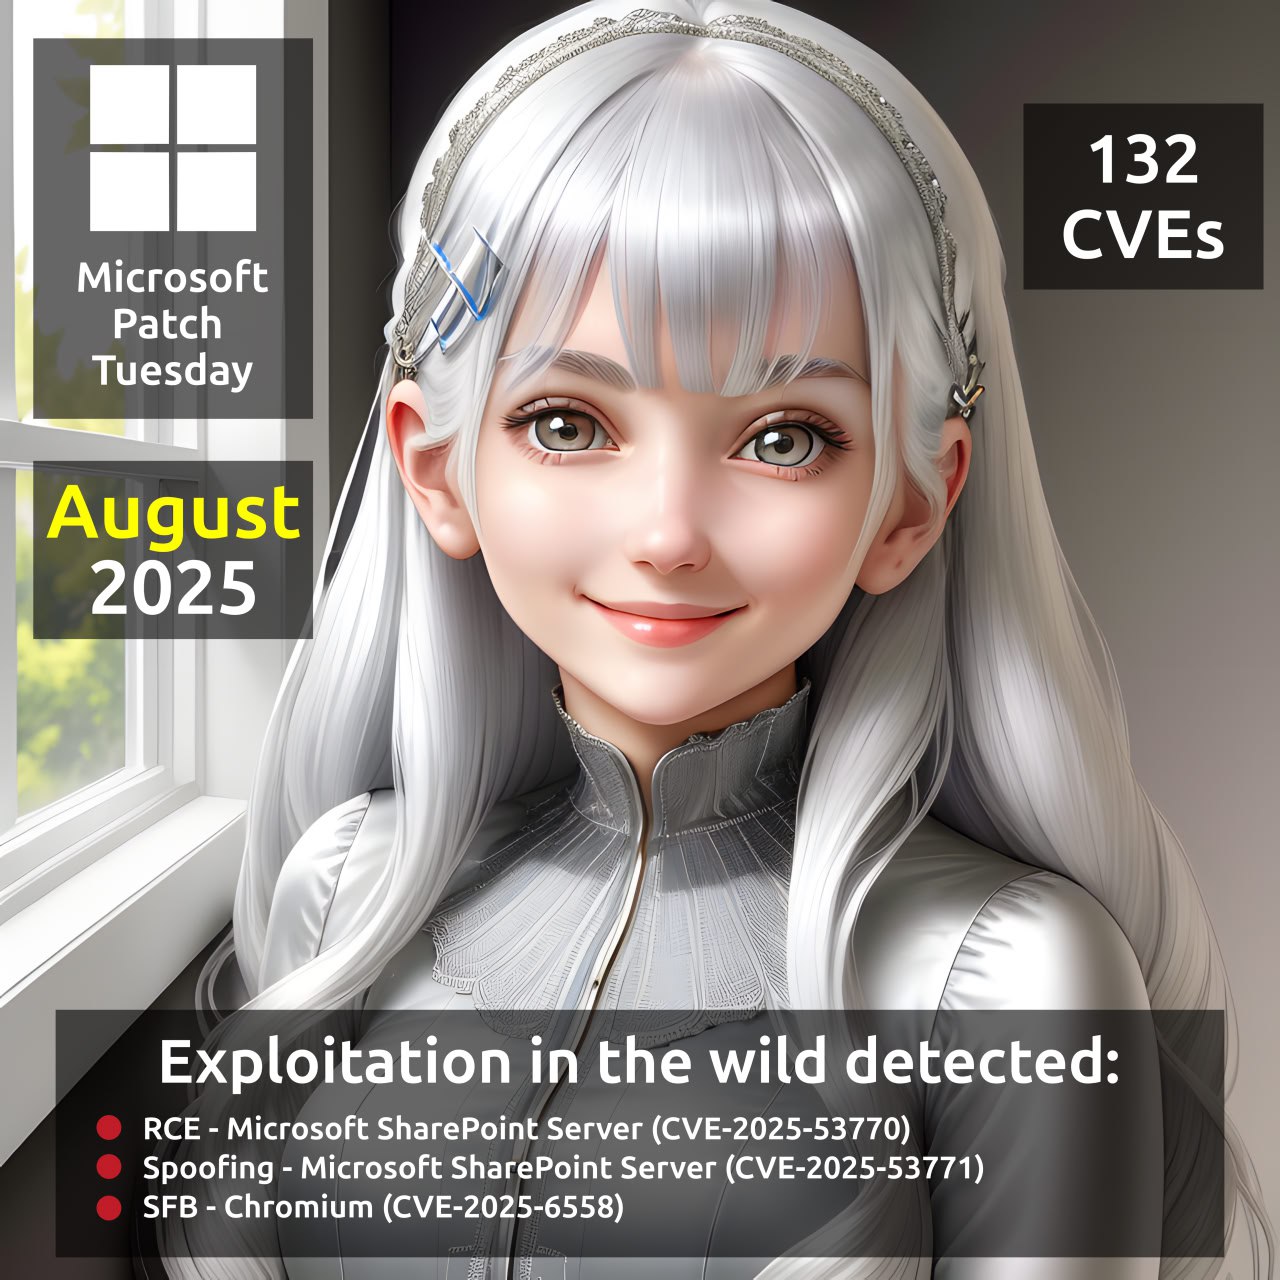
August Microsoft Patch Tuesday. A total of 132 vulnerabilities, 20 fewer than in July. Of these, 25 were added between the July and August MSPT. Three are actively exploited, including two related to the trending SharePoint "ToolShell" flaw, exploited since July 17.

🔻 RCE - Microsoft SharePoint Server (CVE-2025-53770)
🔻 Spoofing - Microsoft SharePoint Server (CVE-2025-53771)

Another actively exploited vulnerability affects Chromium:

🔻SFB - Chromium (CVE-2025-6558)

Notable among the rest, without public exploits or exploitation signs, are:

🔹 RCE - SharePoint (CVE-2025-49712), GDI+ (CVE-2025-53766), Windows Graphics Component (CVE-2025-50165), DirectX Graphics Kernel (CVE-2025-50176), Microsoft Office (CVE-2025-53731, CVE-2025-53740), MSMQ (CVE-2025-53144, CVE-2025-53145, CVE-2025-50177)
🔹 EoP - Kerberos (CVE-2025-53779), NTLM (CVE-2025-53778)

🗒 Full Vulristics report

На русском