Tag Archives: Vulristics

First impressions of the March Microsoft Patch Tuesday

First impressions of the March Microsoft Patch Tuesday
First impressions of the March Microsoft Patch TuesdayFirst impressions of the March Microsoft Patch TuesdayFirst impressions of the March Microsoft Patch TuesdayFirst impressions of the March Microsoft Patch TuesdayFirst impressions of the March Microsoft Patch TuesdayFirst impressions of the March Microsoft Patch TuesdayFirst impressions of the March Microsoft Patch Tuesday

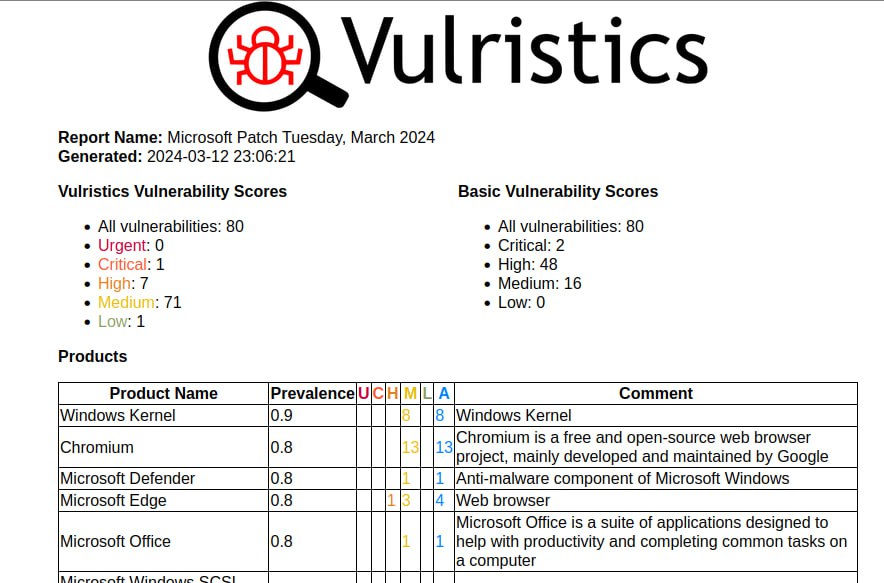
First impressions of the March Microsoft Patch Tuesday. So far I have not seen anything overtly critical. There are 80 vulnerabilities in total, including 20 added between the February and March MSPT.

With PoC there is only one:

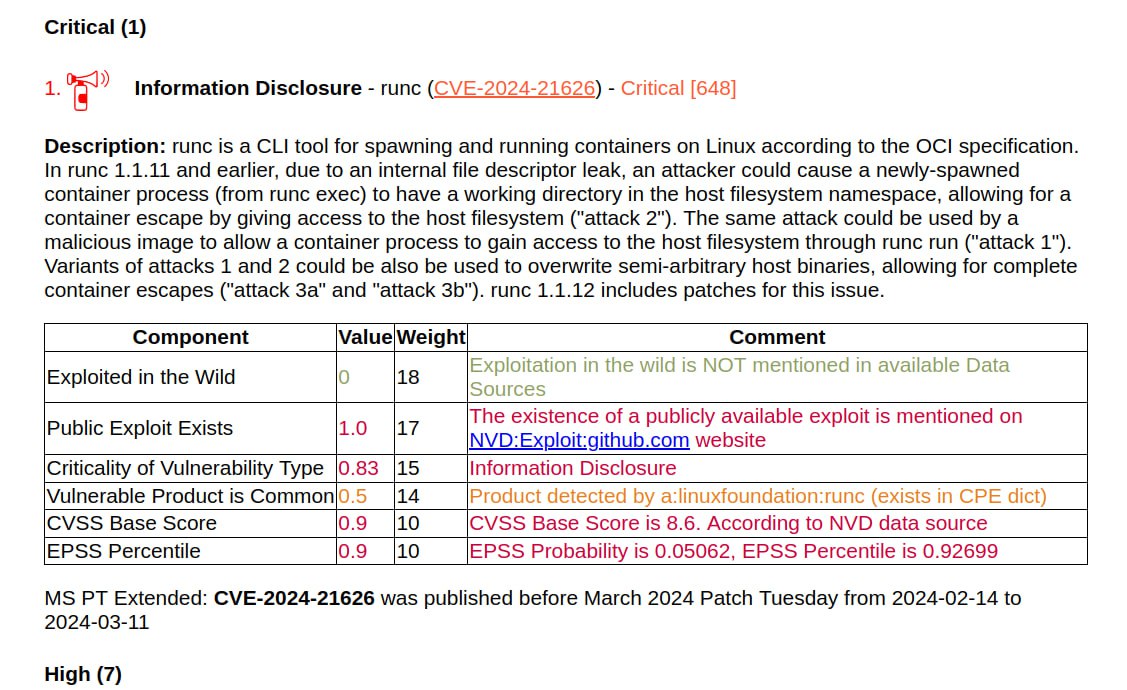
🔻 Information Disclosure - runc (CVE-2024-21626). It allows an attacker to escape from the container. What does Microsoft have to do with it? The vulnerability has been fixed in Azure Kubernetes Service and CBL-Mariner (Microsoft's internal Linux distribution).

For the rest, there are no signs of active exploitation or the existence of a PoC yet.

We can pay attention to the following:

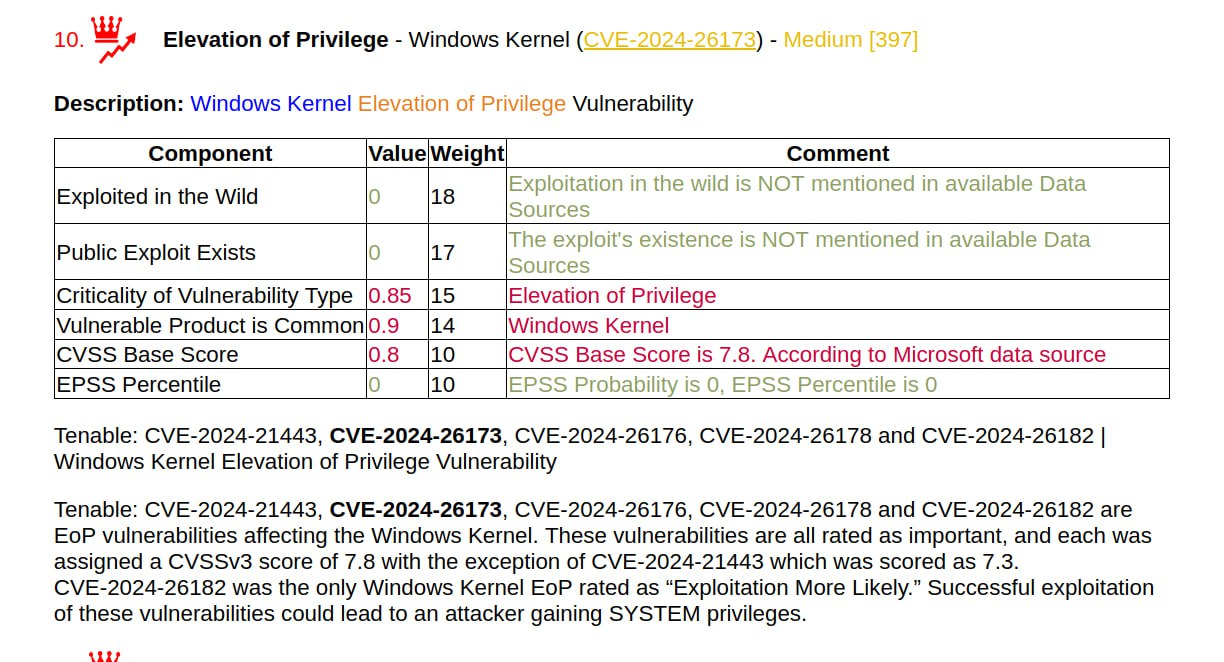
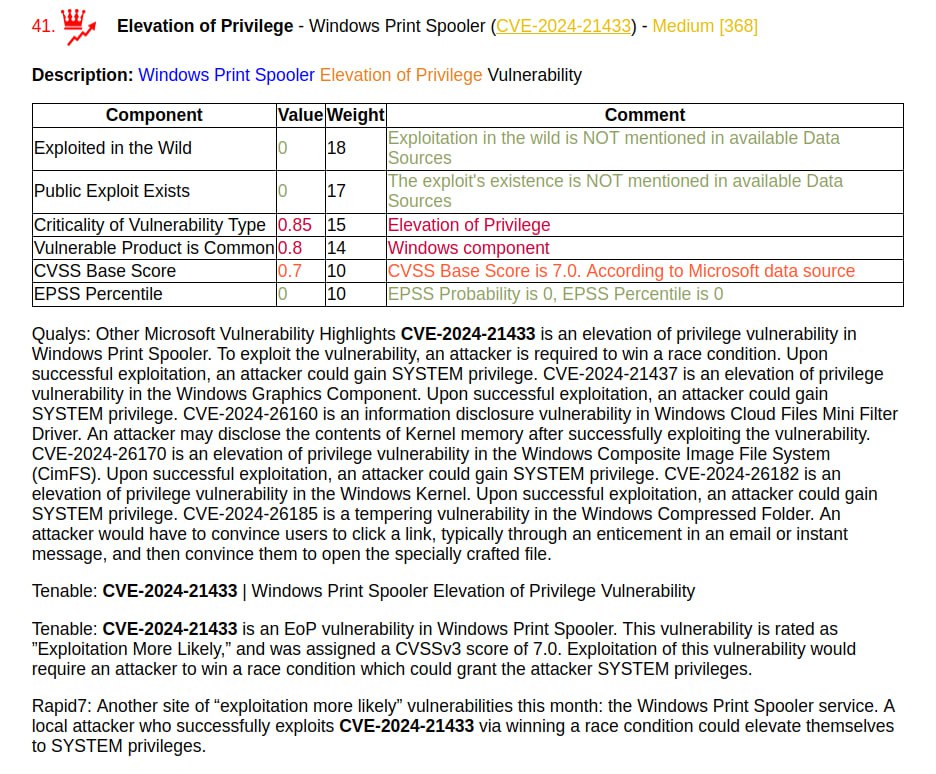
🔸 Elevation of Privilege - Windows Kernel (CVE-2024-21443, CVE-2024-26173, CVE-2024-26176, CVE-2024-26178, CVE-2024-26182). Such vulnerabilities often become exploitable recently. The same applies to Elevation of Privilege - Windows Print Spooler (CVE-2024-21433).
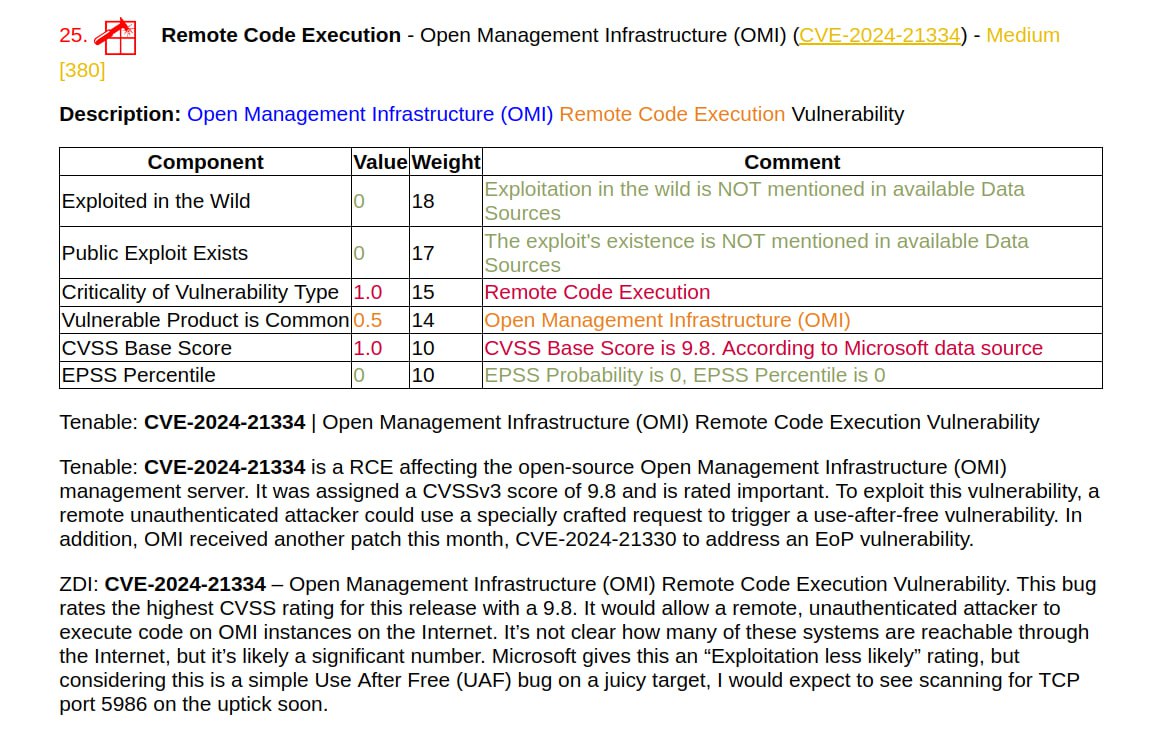
🔸 Remote Code Execution - Open Management Infrastructure (OMI) (CVE-2024-21334). CVSS 9.8 and ZDI write that "it would allow a remote, unauthenticated attacker to execute code on OMI instances on the Internet". Perhaps such instances are indeed often accessible via the Internet, this requires research. 🤷‍♂️
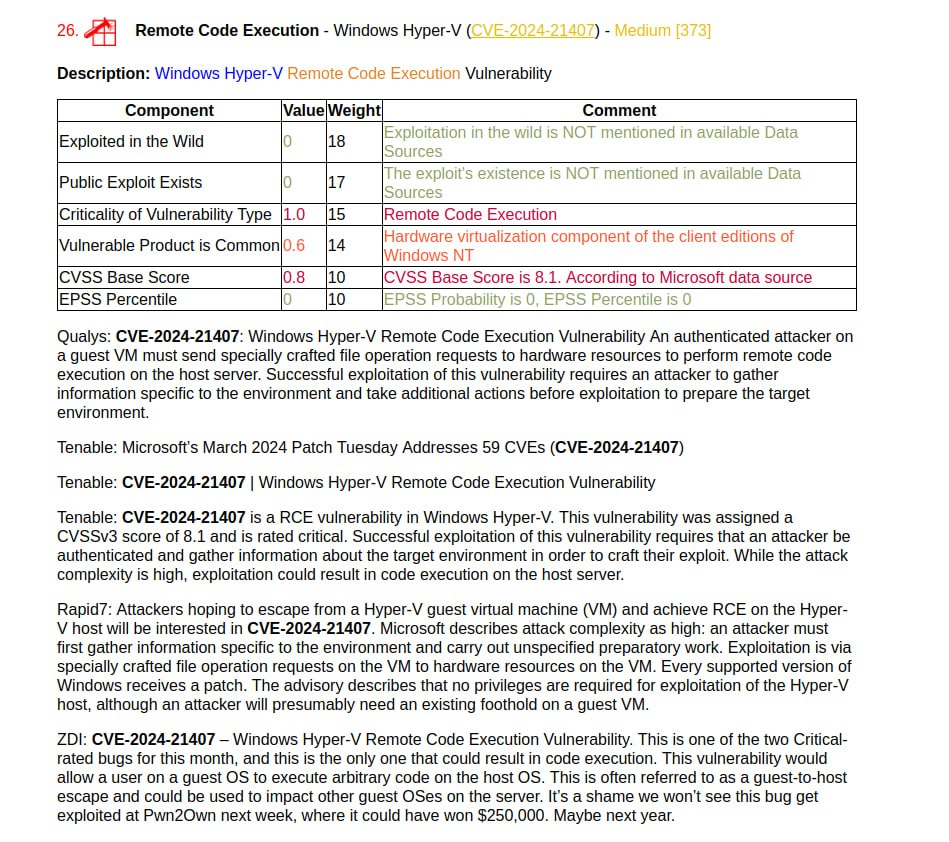
🔸 Remote Code Execution - Windows Hyper-V (CVE-2024-21407). This "guest-to-host escape" vulnerability was highlighted by everyone: Qualys, Tenable, Rapid7, ZDI.
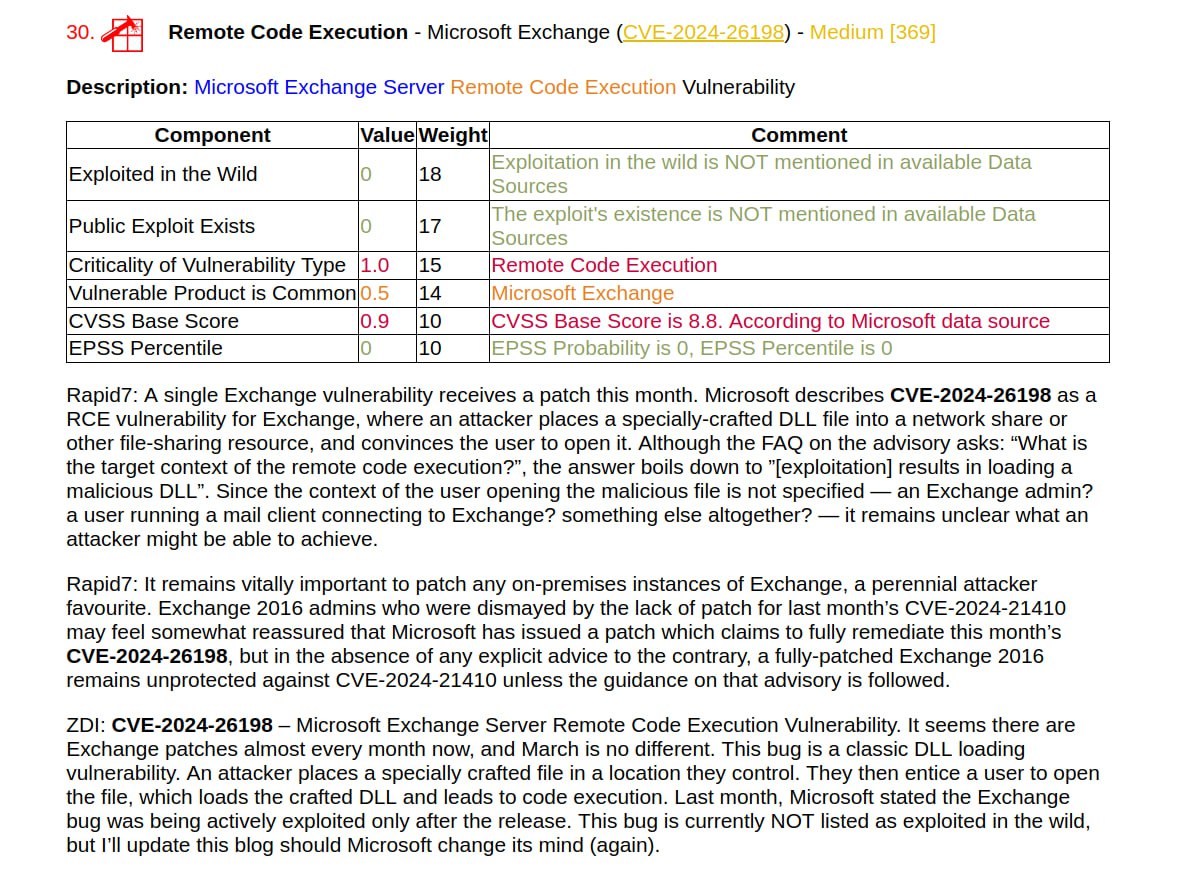
🔸 Remote Code Execution - Microsoft Exchange (CVE-2024-26198). This is a "DLL loading" vulnerability. The details are still unclear, but I wouldn’t be surprised if there will be a detailed write-up on it soon.
🗒 Vulristics report

На русском

October 2023: back to Positive Technologies, Vulristics updates, Linux Patch Wednesday, Microsoft Patch Tuesday, PhysTech VM lecture

October 2023: back to Positive Technologies, Vulristics updates, Linux Patch Wednesday, Microsoft Patch Tuesday, PhysTech VM lecture. Hello everyone! October was an interesting and busy month for me. I started a new job, worked on my open source Vulristics project, and analyzed vulnerabilities using it. Especially Linux vulnerabilities as part of my new Linux Patch Wednesday project. And, of course, analyzed Microsoft Patch Tuesday as well. In addition, at the end of October I was a guest lecturer at MIPT/PhysTech university. But first thing first.

Alternative video link (for Russia): https://vk.com/video-149273431_456239138

Continue reading →

September 2023: VM courses, Bahasa Indonesia, Russian Podcasts, Goodbye Tinkoff, MS Patch Tuesday, Qualys TOP 20, Linux, Forrester, GigaOm, R-Vision VM

September 2023: VM courses, Bahasa Indonesia, Russian Podcasts, Goodbye Tinkoff, MS Patch Tuesday, Qualys TOP 20, Linux, Forrester, GigaOm, R-Vision VM. Hello everyone! On the last day of September, I decided to record another retrospective episode on how my Vulnerability Management month went.

Alternative video link (for Russia): https://vk.com/video-149273431_456239136

September was quite a busy month for me.

Continue reading →

August 2023: GitHub PoCs, Vulristics, Qualys First-Party, Tenable ExposureAI, SC Awards and Rapid7, Anglo-Saxon list, MS Patch Tuesday, WinRAR, Juniper

August 2023: GitHub PoCs, Vulristics, Qualys First-Party, Tenable ExposureAI, SC Awards and Rapid7, Anglo-Saxon list, MS Patch Tuesday, WinRAR, Juniper. Hello everyone! This month I decided NOT to make an episode completely dedicated to Microsoft Patch Tuesday. Instead, this episode will be an answer to the question of how my Vulnerability Management month went. A retrospection of some kind.

Alternative video link (for Russia): https://vk.com/video-149273431_456239134

Continue reading →

Microsoft Patch Tuesday July 2023: Vulristics improvements, Office RCE, SFB SmartScreen and Outlook, EoP MSHTML and ERS, other RCEs

Microsoft Patch Tuesday July 2023: Vulristics improvements, Office RCE, SFB SmartScreen and Outlook, EoP MSHTML and ERS, other RCEs. Hello everyone! This episode will be about Microsoft Patch Tuesday for July 2023, including vulnerabilities that were added between June and July Patch Tuesdays.

Alternative video link (for Russia): https://vk.com/video-149273431_456239131

As usual, I use my open source Vulristics project to analyse and prioritize vulnerabilities.

Continue reading →

Vulristics News: EPSS v3 Support, Integration into Cloud Advisor

Vulristics News: EPSS v3 Support, Integration into Cloud Advisor. Hello everyone! This episode will focus on the news from my open source Vulristics project for vulnerability analysis and prioritization.

Alternative video link (for Russia): https://vk.com/video-149273431_456239122

EPSS v3

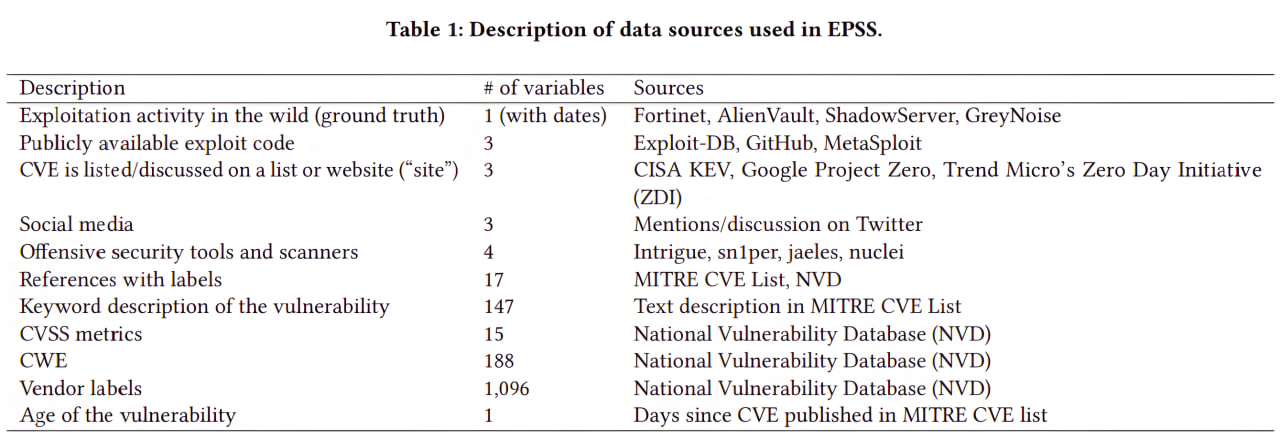
The third iteration of the Exploit Prediction Scoring System (EPSS) was released in March. It is stated that EPSS has become 82% better. There is a pretty cool and detailed article about the changes. For example, EPSS Team began to analyze not 16 parameters of vulnerabilities, but 1164. I have a suspicion that most of these properties are vendor labels, as in the table.

But trying to figure out how it actually works is not very promising. After all, this is the output of some neural network. So there is no algorithm there. In terms of complexity and incomprehensibility, this is already similar to Tenable VPR. But the fact that EPSS is available for free redeems everything. 😇 By the way, the article mentions Tenable VPR and other commercial scores and criticizes them for their proprietary nature, public inaccessibility, and the fact that these scores are partly based on expert opinion, and not just on data.

Continue reading →

Microsoft Patch Tuesday January 2023: ALPC EoP, Win Backup EoP, LocalPotato, Exchange, Remote RCEs

Microsoft Patch Tuesday January 2023: ALPC EoP, Win Backup EoP, LocalPotato, Exchange, Remote RCEs. Hello everyone! This episode will be about Microsoft Patch Tuesday for January 2023, including vulnerabilities that were added between December and January Patch Tuesdays.

Alternative video link (for Russia): https://vk.com/video-149273431_456239115

As usual, I use my open source Vulristics project to analyse and prioritize vulnerabilities. I took the comments about the vulnerabilities from the Qualys, Nessus, Rapid7 and ZDI Patch Tuesday reviews.

Continue reading →